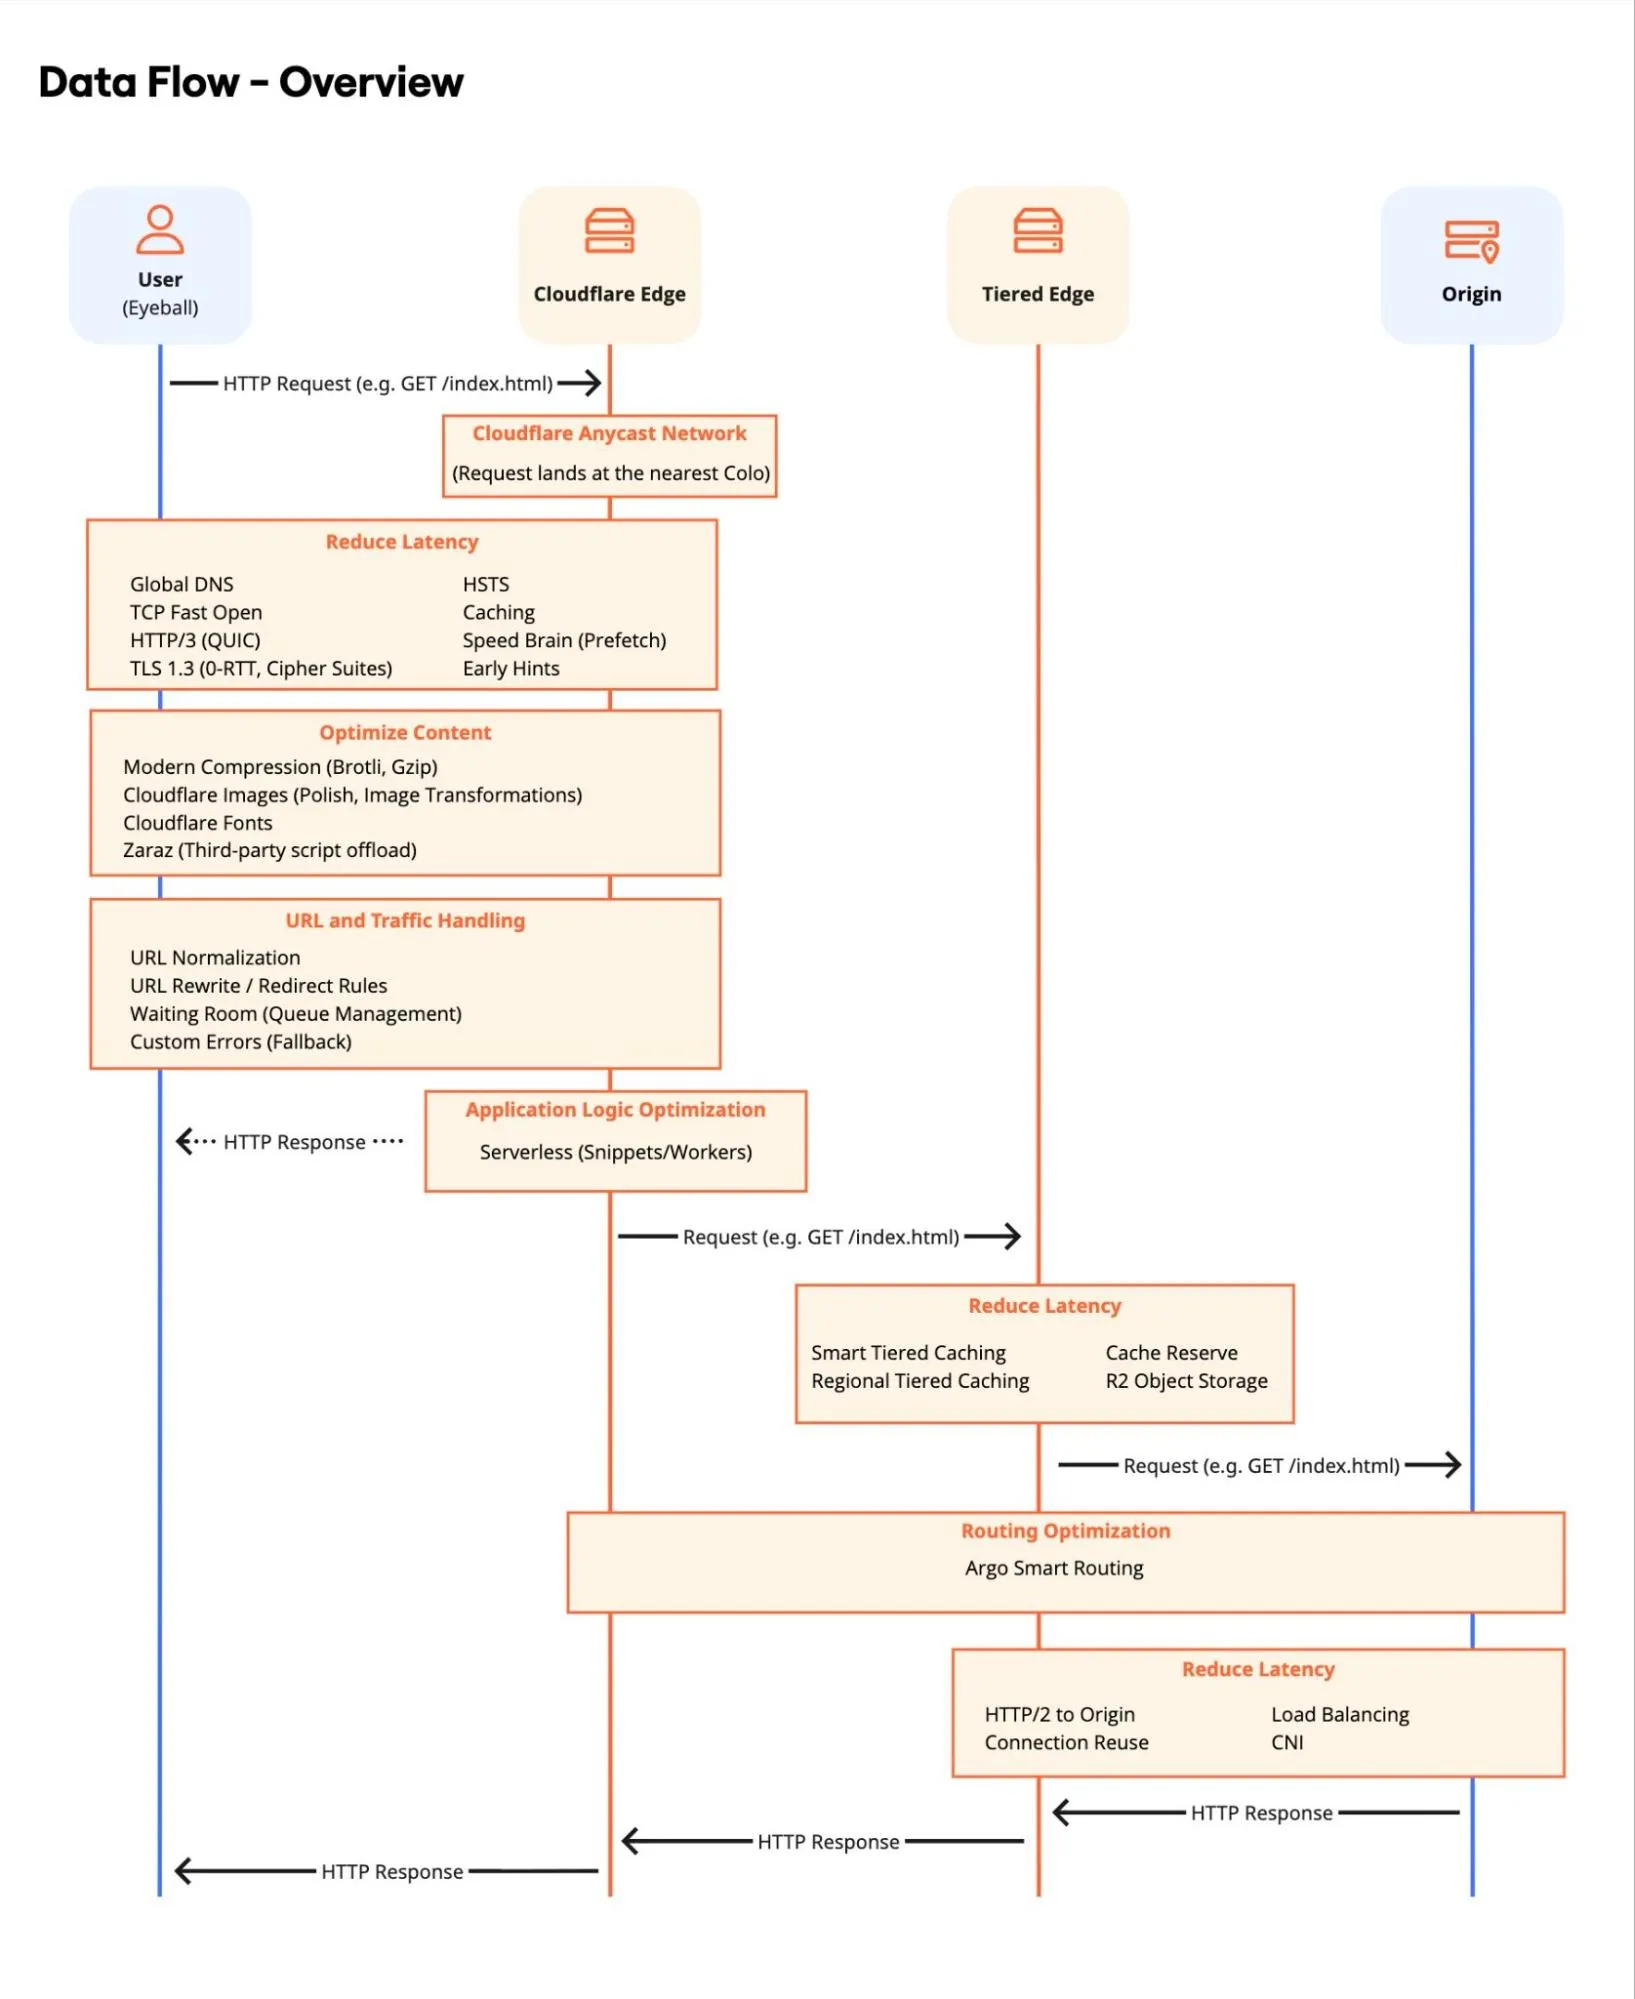
DDoS là gì? Cloudflare bảo vệ website thế nào (không thuật ngữ nặng) What is a DDoS? How Cloudflare protects your site in plain language What is a DDoS? How Cloudflare protects your site in plain language
DDoS giống hàng nghìn người chen cửa hàng chỉ để làm tắc — không mua gì. Cloudflare đứng trước cửa, phân loại và chặn làn sóng request vô nghĩa trước origin. A DDoS is like thousands of people crowding your shop door just to block it — not to buy. Cloudflare stands at the door, sorting and blocking meaningless request waves before your origin. A DDoS is like thousands of people crowding your shop door just to block it — not to buy. Cloudflare stands at the door, sorting and blocking meaningless request waves before your origin.

Bảo vệ mạng hybrid cloud với Magic Transit Protect hybrid cloud networks with Cloudflare Magic Transit Protect hybrid cloud networks with Cloudflare Magic Transit
Magic Transit cung cấp bảo vệ DDoS in-line trên cloud và tăng tốc traffic cho mọi mạng hướng Internet. Cloudflare Magic Transit provides cloud-native, in-line DDoS protection, and traffic acceleration for all Internet-facing networks. Cloudflare Magic Transit provides cloud-native, in-line DDoS protection, and traffic acceleration for all Internet-facing networks.
Thuật ngữ: Concepts: Concepts: Magic Transit · DDoS · Anycast · Hybrid cloud
Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Mạng Network Network
DDoS là gì — tại sao website “chết” dù server vẫn bật? What is DDoS — why does a site “die” while the server is still on? What is DDoS — why does a site “die” while the server is still on?
DDoS (Distributed Denial of Service) là kiểu tấn công làm website hoặc API quá tải bằng lượng request khổng lồ — thường từ nhiều máy bị lợi dụng hoặc botnet. Mục tiêu không phải đánh cắp mật khẩu ngay lập tức, mà làm dịch vụ chậm hoặc sập để gây thiệt hại uy tín, doanh thu, hoặc che hành vi khác. DDoS (Distributed Denial of Service) floods a website or API with huge request volume — often from compromised machines or botnets. The goal is not always instant password theft; it is to slow or knock the service offline, hurting reputation, revenue, or masking other activity. DDoS (Distributed Denial of Service) floods a website or API with huge request volume — often from compromised machines or botnets. The goal is not always instant password theft; it is to slow or knock the service offline, hurting reputation, revenue, or masking other activity.
Hình ảnh dễ nhớ: cửa hàng bình thường nhận vài chục khách/giờ. Một ngày có vài nghìn người đứng chen cửa, hỏi giá vô ích, không vào mua — nhân viên kiệt sức, khách thật không lọt được. Server origin của bạn cũng có giới hạn kết nối và CPU; DDoS khai thác giới hạn đó. Easy metaphor: a normal shop serves dozens of visitors per hour. One day thousands crowd the door, ask useless questions, never buy — staff exhaust themselves and real customers cannot enter. Your origin server has connection and CPU limits too; DDoS exploits those limits. Easy metaphor: a normal shop serves dozens of visitors per hour. One day thousands crowd the door, ask useless questions, never buy — staff exhaust themselves and real customers cannot enter. Your origin server has connection and CPU limits too; DDoS exploits those limits.
Các bài trên blog.cloudflare.com về DDoS nhấn mạnh quy mô: tấn công lớn có thể vượt sức một máy chủ đơn lẻ hoặc một đường truyền. Đó là lý do nhiều tổ chức đặt lớp bảo vệ trước origin — không chỉ dựa vào hosting “mạnh hơn một chút”. Cloudflare Blog posts on DDoS stress scale: large attacks can exceed what one server or one uplink can handle. That is why many organizations place protection in front of origin — not only “a slightly bigger hosting plan.” Cloudflare Blog posts on DDoS stress scale: large attacks can exceed what one server or one uplink can handle. That is why many organizations place protection in front of origin — not only “a slightly bigger hosting plan.”
Bảo vệ mạng hybrid cloud với Magic Transit Protect hybrid cloud networks with Cloudflare Magic Transit Protect hybrid cloud networks with Cloudflare Magic Transit
Magic Transit cung cấp bảo vệ DDoS in-line trên cloud và tăng tốc traffic cho mọi mạng hướng Internet. Cloudflare Magic Transit provides cloud-native, in-line DDoS protection, and traffic acceleration for all Internet-facing networks. Cloudflare Magic Transit provides cloud-native, in-line DDoS protection, and traffic acceleration for all Internet-facing networks.
Thuật ngữ: Concepts: Concepts: Magic Transit · DDoS · Anycast · Hybrid cloud
Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Mạng Network Network
Cloudflare chặn DDoS ở đâu trong đường đi request? Where does Cloudflare block DDoS in the request path? Where does Cloudflare block DDoS in the request path?
Khi site được proxy (đám mây cam), traffic đi qua mạng anycast toàn cầu của Cloudflare trước origin. Lớp chống DDoS có thể nhận diện pattern bất thường — burst request, giao thức lạ, amplification — và hấp thụ hoặc lọc gần nguồn tấn công hơn là để mọi thứ đổ về một IP origin duy nhất. When a site is proxied (orange cloud), traffic hits Cloudflare’s global anycast network before origin. DDoS mitigation can spot abnormal patterns — request bursts, odd protocols, amplification — and absorb or filter closer to the attack source instead of dumping everything on one origin IP. When a site is proxied (orange cloud), traffic hits Cloudflare’s global anycast network before origin. DDoS mitigation can spot abnormal patterns — request bursts, odd protocols, amplification — and absorb or filter closer to the attack source instead of dumping everything on one origin IP.
Với hầu hết khách hàng proxy HTTP/HTTPS, nhiều biện pháp chạy tự động — bạn không cần “bật nút chống DDoS” riêng cho từng đợt nhỏ. Điều đó khác với WAF tinh chỉnh theo ứng dụng: DDoS tập trung vào khối lượng và hành vi mạng; WAF tập trung vào lỗ hổng HTTP như injection. For most proxied HTTP/HTTPS customers, many measures run automatically — you do not flip a separate “anti-DDoS switch” for every small wave. That differs from app-tuned WAF: DDoS focuses on volume and network behavior; WAF focuses on HTTP flaws like injection. For most proxied HTTP/HTTPS customers, many measures run automatically — you do not flip a separate “anti-DDoS switch” for every small wave. That differs from app-tuned WAF: DDoS focuses on volume and network behavior; WAF focuses on HTTP flaws like injection.
Enterprise hoặc mạng lớn có thể dùng thêm sản phẩm như Magic Transit cho IP range — vượt phạm vi bài này, nhưng cùng triết lý: chặn sớm, phân tán, không để một điểm gãy. Enterprise or large networks may add products like Magic Transit for IP ranges — beyond this post’s scope, but same philosophy: block early, distribute load, avoid a single breaking point. Enterprise or large networks may add products like Magic Transit for IP ranges — beyond this post’s scope, but same philosophy: block early, distribute load, avoid a single breaking point.
Tự động vs phần bạn vẫn nên cấu hình Automatic protection vs what you should still configure Automatic protection vs what you should still configure
Tự động (với proxy): lớp chống DDoS network/application cơ bản, anycast hấp thụ traffic, một phần bot và rate anomaly. Bạn vẫn nên: bật đám mây cam cho hostname công khai; giữ origin không lộ IP trực tiếp nếu có thể; theo dõi Security Analytics khi có sự cố. Automatic (with proxy): baseline network/application DDoS mitigation, anycast absorption, some bot and rate anomaly handling. You should still: orange-cloud public hostnames; avoid exposing origin IP when possible; watch Security Analytics during incidents. Automatic (with proxy): baseline network/application DDoS mitigation, anycast absorption, some bot and rate anomaly handling. You should still: orange-cloud public hostnames; avoid exposing origin IP when possible; watch Security Analytics during incidents.
Cấu hình thêm khi cần: WAF managed rules cho tấn công lớp ứng dụng; rate limiting cho login/API; Bot Management cho chiến dịch quét; firewall origin chỉ cho phép Cloudflare (và IP admin). DDoS “thô” và WAF/bot bổ sung cho nhau — không thay thế. Extra configuration when needed: WAF managed rules for application-layer attacks; rate limiting on login/API; Bot Management during scan campaigns; origin firewall allowing only Cloudflare (and admin IPs). Raw DDoS mitigation and WAF/bot layers complement each other. Extra configuration when needed: WAF managed rules for application-layer attacks; rate limiting on login/API; Bot Management during scan campaigns; origin firewall allowing only Cloudflare (and admin IPs). Raw DDoS mitigation and WAF/bot layers complement each other.
Nếu bạn mới học Application Services trên hub: thứ tự hợp lý là DNS/proxy → hiểu DDoS tự động → WAF baseline → cache đúng chỗ. Đừng bỏ qua proxy xám rồi thắc mắc vì sao không có lớp bảo vệ HTTP. If you are new to the Application Services track on this hub: a sensible order is DNS/proxy → understand automatic DDoS → WAF baseline → cache in the right places. Do not stay grey-cloud and wonder why HTTP protection never appears. If you are new to the Application Services track on this hub: a sensible order is DNS/proxy → understand automatic DDoS → WAF baseline → cache in the right places. Do not stay grey-cloud and wonder why HTTP protection never appears.
Khi bị tấn công thật: ghi lại thời điểm, hostname, và biểu đồ request; tránh restart origin liên tục mà không xem log; liên hệ support nếu gói của bạn có kênh khẩn cấp. Panic reboot hiếm khi là chiến lược DDoS tốt. During a real attack: note time, hostname, and request charts; avoid endless origin reboots without reading logs; contact support if your plan has an emergency channel. Panic reboots are rarely a good DDoS strategy. During a real attack: note time, hostname, and request charts; avoid endless origin reboots without reading logs; contact support if your plan has an emergency channel. Panic reboots are rarely a good DDoS strategy.
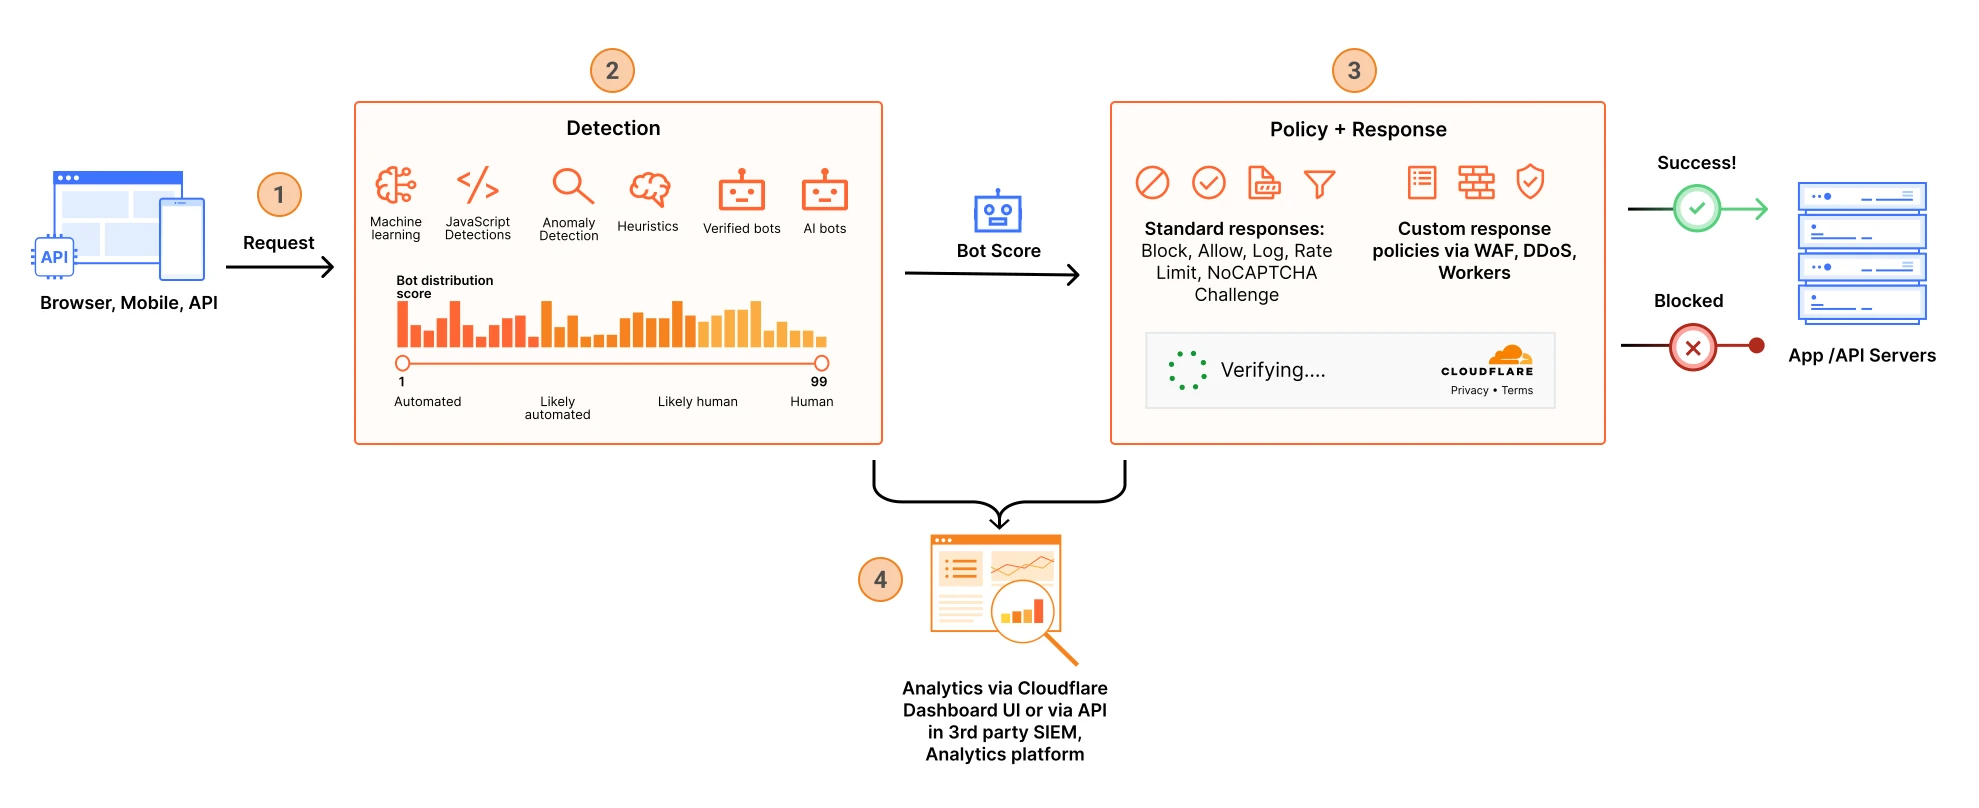
Quản lý bot Bot management Bot management
Luồng phát hiện, chấm điểm và xử lý bot traffic trên edge — nền tảng cho WAF, rate limit và Bot Management. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots.
Thuật ngữ: Concepts: Concepts: Bot score · Super Bot Fight Mode · WAF · Rate limiting
Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Bot Bots Bots
Dấu hiệu nhận biết và bước đầu tự vệ Warning signs and first self-defense steps Warning signs and first self-defense steps
Dấu hiệu: trang timeout đồng loạt, CPU origin 100% dù ít người dùng thật, băng thông tăng đột biến, log đầy request giống nhau từ nhiều IP. Có thể là DDoS, crawler hung, hoặc lỗi deploy — cần nhìn dashboard trước khi kết luận. Signs: widespread timeouts, origin CPU at 100% with few real users, bandwidth spikes, logs full of similar requests from many IPs. Could be DDoS, an aggressive crawler, or a bad deploy — check the dashboard before concluding. Signs: widespread timeouts, origin CPU at 100% with few real users, bandwidth spikes, logs full of similar requests from many IPs. Could be DDoS, an aggressive crawler, or a bad deploy — check the dashboard before concluding.
Bước đầu: xác nhận proxy đang bật; bật “Under Attack Mode” tạm thời nếu Cloudflare gợi ý trong sự cố lớn (có thể thêm challenge cho visitor); siết rate limit đường dẫn bị nhắm; purge cache nếu nội dung tĩnh bị lạm dụng. Đọc bài WAF và CDN trên hub để hiểu lớp kế tiếp. First steps: confirm proxy is on; temporarily enable Under Attack Mode during major incidents (may add visitor challenges); tighten rate limits on targeted paths; purge cache if static content is abused. Read the WAF and CDN posts on this hub for the next layers. First steps: confirm proxy is on; temporarily enable Under Attack Mode during major incidents (may add visitor challenges); tighten rate limits on targeted paths; purge cache if static content is abused. Read the WAF and CDN posts on this hub for the next layers.
Phòng lâu dài: không publish origin IP; dùng CDN/cache cho asset nặng; cập nhật phần mềm; có kế hoạch incident đơn giản (ai xem dashboard, ai nói với khách). DDoS là rủi ro kinh doanh — chuẩn bị nhẹ vẫn tốt hơn học trong đợt tấn công đầu tiên. Long-term: do not publish origin IP; use CDN/cache for heavy assets; patch software; keep a simple incident plan (who watches the dashboard, who talks to customers). DDoS is a business risk — light preparation beats learning only during the first attack. Long-term: do not publish origin IP; use CDN/cache for heavy assets; patch software; keep a simple incident plan (who watches the dashboard, who talks to customers). DDoS is a business risk — light preparation beats learning only during the first attack.
Câu hỏi thường gặp Frequently asked questions Frequently asked questions
DDoS và hack database có giống nhau không? Is DDoS the same as hacking a database? Is DDoS the same as hacking a database?
Không. DDoS nhắm làm dịch vụ quá tải hoặc không truy cập được. Hack database thường là lợi dụng lỗ hổng phần mềm hoặc credential yếu. Cả hai đều nguy hiểm nhưng cần biện pháp khác nhau — WAF và vá lỗi quan trọng cho lớp ứng dụng. No. DDoS aims to overload or make a service unreachable. Database hacks usually exploit software bugs or weak credentials. Both are serious but need different defenses — WAF and patching matter for the application layer. No. DDoS aims to overload or make a service unreachable. Database hacks usually exploit software bugs or weak credentials. Both are serious but need different defenses — WAF and patching matter for the application layer.
Site DNS only (xám) có được bảo vệ DDoS HTTP không? Does a DNS-only (grey) site get HTTP DDoS protection? Does a DNS-only (grey) site get HTTP DDoS protection?
Lớp bảo vệ HTTP/DDoS qua proxy không áp dụng khi traffic không đi qua Cloudflare. Bạn vẫn dùng DNS Cloudflare, nhưng request thẳng origin — cần biện pháp khác hoặc bật proxy cho hostname web. HTTP/DDoS protection through the proxy does not apply when traffic does not pass Cloudflare. You still use Cloudflare DNS, but requests hit origin directly — you need other measures or orange-cloud for web hostnames. HTTP/DDoS protection through the proxy does not apply when traffic does not pass Cloudflare. You still use Cloudflare DNS, but requests hit origin directly — you need other measures or orange-cloud for web hostnames.
Under Attack Mode có ảnh hưởng khách thật không? Does Under Attack Mode affect real visitors? Does Under Attack Mode affect real visitors?
Có thể — thường thêm bước xác minh (challenge) trước khi vào site. Dùng khi đang bị tấn công lớn, tắt lại khi ổn định. Cân bằng giữa bảo vệ và trải nghiệm người dùng. It can — often by adding a verification challenge before the site loads. Use it during major attacks and turn it off when stable. Balance protection with user experience. It can — often by adding a verification challenge before the site loads. Use it during major attacks and turn it off when stable. Balance protection with user experience.
Học tiếp trên hub (on-page backlinks) Keep learning on this hub (on-page links) Keep learning on this hub (on-page links)
- WAF là gì? (trang sản phẩm) What is WAF? (product page) What is WAF? (product page)
- Lộ trình Application Services Application Services track Application Services track
- Use case: bảo vệ website Use case: protect website Use case: protect website
- Use case: chống DDoS Use case: defend DDoS attacks Use case: defend DDoS attacks
- Cloudflare 101 Cloudflare 101 Cloudflare 101
- Sản phẩm: DDoS Protection Product: DDoS Protection Product: DDoS Protection
Nguồn tham khảo (blog.cloudflare.com) Sources (blog.cloudflare.com) Sources (blog.cloudflare.com)
Nội dung được viết lại để dễ hiểu hơn; luôn đọc bài gốc trên blog.cloudflare.com và docs chính thức khi cần chi tiết kỹ thuật hoặc cập nhật mới nhất. Content is rewritten for clarity; always read the original posts on blog.cloudflare.com and official docs for technical detail or the latest updates. Content is rewritten for clarity; always read the original posts on blog.cloudflare.com and official docs for technical detail or the latest updates.