Lộ trình đang học Current learning path Current learning path

Application Services Application Services Application Services

Làm đúng từng bước trên dashboard: zone chạy, HTTPS Full (strict), WAF log rồi block, cache không phá session. Click through the dashboard: a live zone, Full (strict) HTTPS, WAF log-then-block, cache that does not break sessions. ចុចតាម dashboard៖ zone កំពុងដំណើរការ, HTTPS Full (strict), WAF log-then-block, cache ដែលមិនបំបែក session។

Về trang lộ trình Track home Track home

Application Services Application Services Application Services

Follow-along: DNS → proxy → SSL → WAF → cache — rồi mới rẽ API Shield hoặc Load Balancing Follow-along: DNS → proxy → SSL → WAF → cache — then branch to API Shield or Load Balancing Follow-along: DNS → proxy → SSL → WAF → cache — បន្ទាប់មកទើបបែកផ្លូវទៅ API Shield ឬ Load Balancing

Lộ trình follow-along cho team đã có website, web app hoặc API public. Làm theo thứ tự — mỗi phần xây trên phần trước. Dừng sau bất kỳ phần bắt buộc nào vẫn có giá trị. Use case (bảo vệ site / API / DDoS) là cửa chọn; track này là đường làm. A follow-along path for teams with a live website, web app, or public API. Work in order — each part builds on the last. Stopping after any required part still leaves something useful. Use cases (protect site / API / DDoS) are the doorway; this track is the how-to. ផ្លូវ follow-along សម្រាប់ team ដែលមាន website, web app ឬ API សាធារណៈ កំពុងដំណើរការ។ ធ្វើតាមលំដាប់ — ផ្នែកនីមួយៗសង់លើផ្នែកមុន។ បញ្ឈប់បន្ទាប់ពីផ្នែកចាំបាច់ណាមួយ នៅតែទុកអ្វីដែលមានប្រយោជន៍។ ករណីប្រើប្រាស់ (ការពារ site / API / DDoS) គឺជាច្រកចូល; track នេះគឺរបៀបធ្វើ។

Ai nên học lộ trình này? Who is this for? Who is this for?

Phù hợp nếu bạn là IT, Security, DevOps, developer vận hành production, hoặc chủ doanh nghiệp có website/app đang chạy thật. A good fit if you are IT, Security, DevOps, a developer operating production, or a business owner with a live website or app. សមស្រប ប្រសិនបើអ្នកជា IT, Security, DevOps, developer ដែលដំណើរការ production ឬម្ចាស់អាជីវកម្មដែលមាន website ឬ app កំពុងដំណើរការ។

Mô hình tư duy Mental model Mental model

Visitor → DNS (NS hoặc CNAME) → Proxy (orange cloud) → SSL/TLS → WAF / Bot / Rate limit → Cache / Speed → Origin. Proxy tắt = chỉ DNS, không WAF/cache. Visitor → DNS (NS or CNAME) → Proxy (orange cloud) → SSL/TLS → WAF / Bot / Rate limit → Cache / Speed → Origin. Proxy off = DNS only, no WAF/cache. Visitor → DNS (NS ឬ CNAME) → Proxy (orange cloud) → SSL/TLS → WAF / Bot / Rate limit → Cache / Speed → Origin។ Proxy បិទ = DNS តែប៉ុណ្ណោះ, គ្មាន WAF/cache។

Bắt đầu tại đây (START HERE) START HERE ចាប់ផ្តើមនៅទីនេះ (START HERE)

Đây là hướng dẫn follow-along. Làm đúng từng bước: click, nhập, checkpoint. Nhãn menu có thể đổi — chọn mục tương đương gần nhất. Use case trên hub giúp chọn đường; đừng rẽ API Shield hay Load Balancing trước khi proxy + SSL + WAF log ổn. This is a follow-along guide. Do exactly what each step says: click, type, checkpoint. Menu labels shift — follow the nearest equivalent. Hub use cases help you choose a path; do not branch into API Shield or Load Balancing before proxy + SSL + WAF log are healthy. នេះជាមគ្គុទេសក៍ follow-along។ ធ្វើតាមពិតប្រាកដនូវអ្វីដែលជំហាននីមួយៗនិយាយ៖ click, type, checkpoint។ ស្លាក menu អាចផ្លាស់ប្តូរ — តាមគោលដៅសមមូលជិតបំផុត។ ករណីប្រើប្រាស់នៅ hub ជួយអ្នកជ្រើសរើសផ្លូវ; កុំបែកផ្លូវទៅ API Shield ឬ Load Balancing មុនពេល proxy + SSL + WAF log មានស្ថិរភាព។

Trước khi Add a site Before you Add a site មុនពេលអ្នក Add a site

  • Domain đang chạy (hoặc staging) và quyền đổi nameserver tại registrar A live domain (or staging) and permission to change nameservers at the registrar A live domain (or staging) and permission to change nameservers at the registrar
  • Screenshot hoặc zone file DNS hiện tại (MX, TXT, SPF/DKIM, verification) Screenshot or zone file of current DNS (MX, TXT, SPF/DKIM, verification) Screenshot or zone file of current DNS (MX, TXT, SPF/DKIM, verification)
  • Quyền SSH/firewall origin nếu sẽ lockdown IP SSH/firewall access to origin if you will lock down IPs SSH/firewall access to origin if you will lock down IPs
  • Ghi: hostname production (www vs apex), path nhạy cảm đầu tiên (/login hoặc /api), plan hiện tại Write down: production hostname (www vs apex), first sensitive path (/login or /api), current plan Write down: production hostname (www vs apex), first sensitive path (/login or /api), current plan
  • Quyết định: full setup (đổi NS) hay partial/CNAME (Business+) Decide: full setup (change NS) or partial/CNAME (Business+) Decide: full setup (change NS) or partial/CNAME (Business+)

Gói nào cần cho từng lớp? Which plan for each layer? Plan មួយណាសម្រាប់ស្រទាប់នីមួយៗ?

Bắt đầu Free để học Phần 1–4. Nâng cấp khi Bot Management, API Shield, Load Balancing hoặc Waiting Room bị greyed out — không đoán feature. Start on Free to learn Parts 1–4. Upgrade when Bot Management, API Shield, Load Balancing, or Waiting Room is greyed out — do not guess entitlements. ចាប់ផ្តើមនៅ Free ដើម្បីរៀនផ្នែក 1–4។ Upgrade ពេល Bot Management, API Shield, Load Balancing ឬ Waiting Room ត្រូវបាន greyed out — កុំទាយ entitlements។

Sơ đồ kiến trúc tham chiếu Reference architecture diagrams Reference architecture diagrams

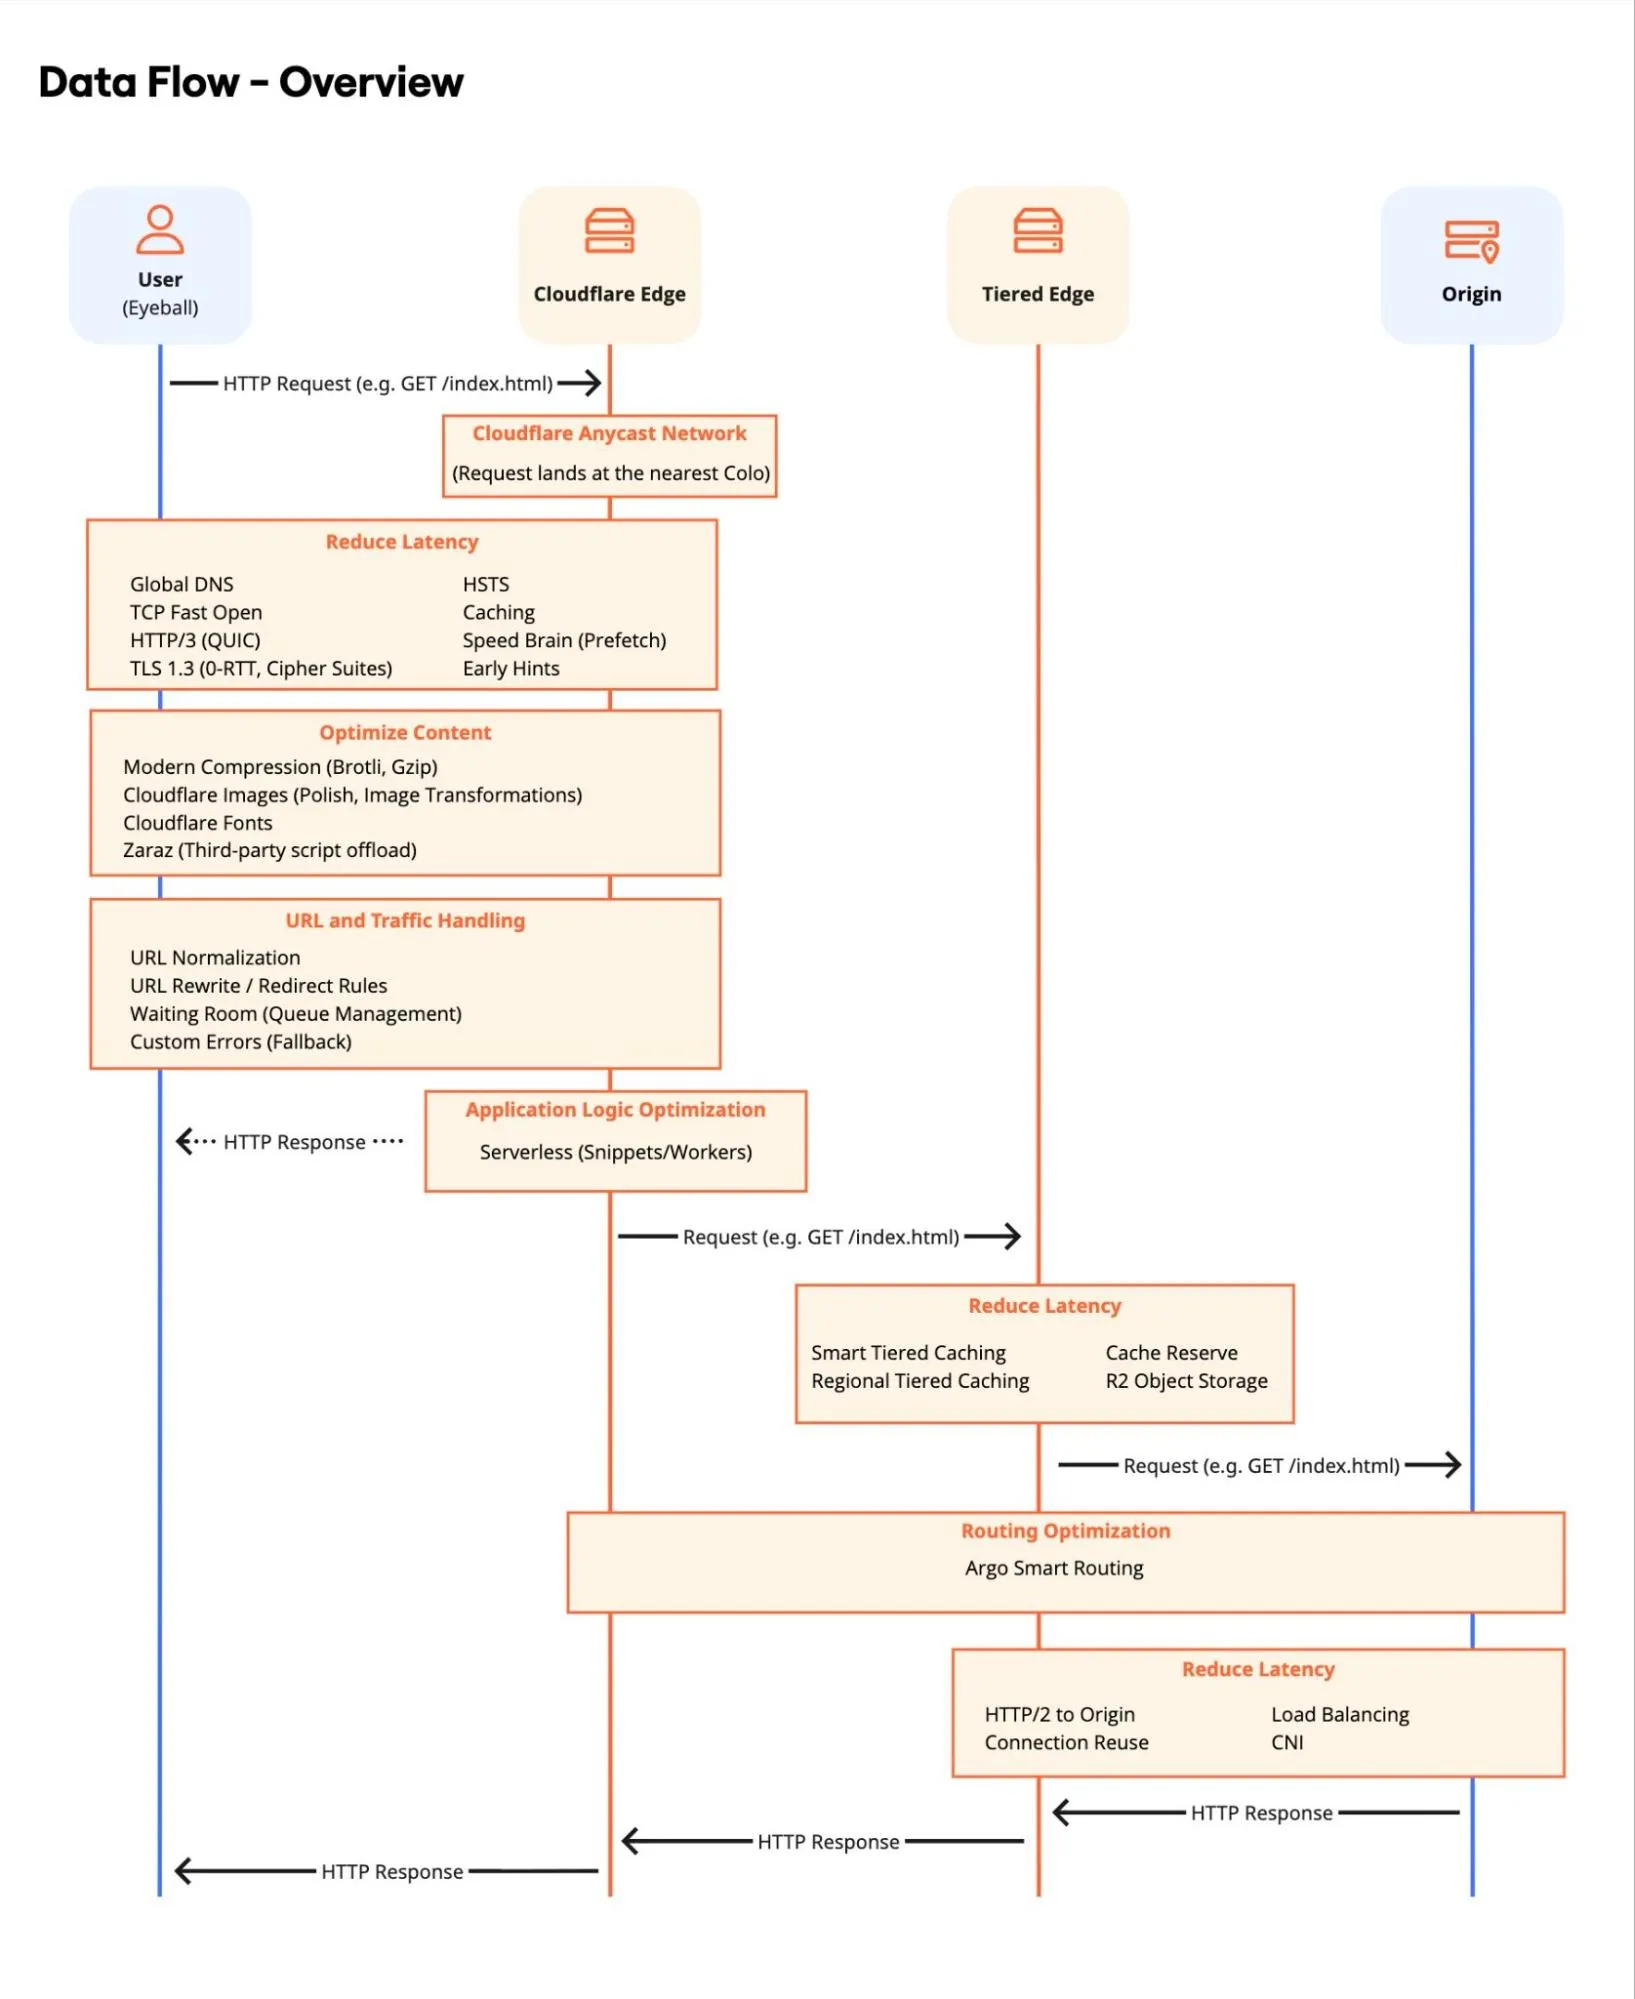
Hình 1: Tổng quan luồng dữ liệu

Thiết kế kiến trúc hiệu năng web phân tán Designing a distributed web performance architecture Designing a distributed web performance architecture

Pattern L7: data flow, cache tiers, deployment models — giảm latency và cải thiện Core Web Vitals. A prescriptive pattern for building a Cloudflare-based L7 performance architecture that reduces latency, raises cache efficiency, and improves Core Web Vitals. A prescriptive pattern for building a Cloudflare-based L7 performance architecture that reduces latency, raises cache efficiency, and improves Core Web Vitals.

Thuật ngữ: Concepts: Concepts: CDN · Cache · Core Web Vitals · Smart Shield · Argo

Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Phân phối nội dung Content Delivery Content Delivery

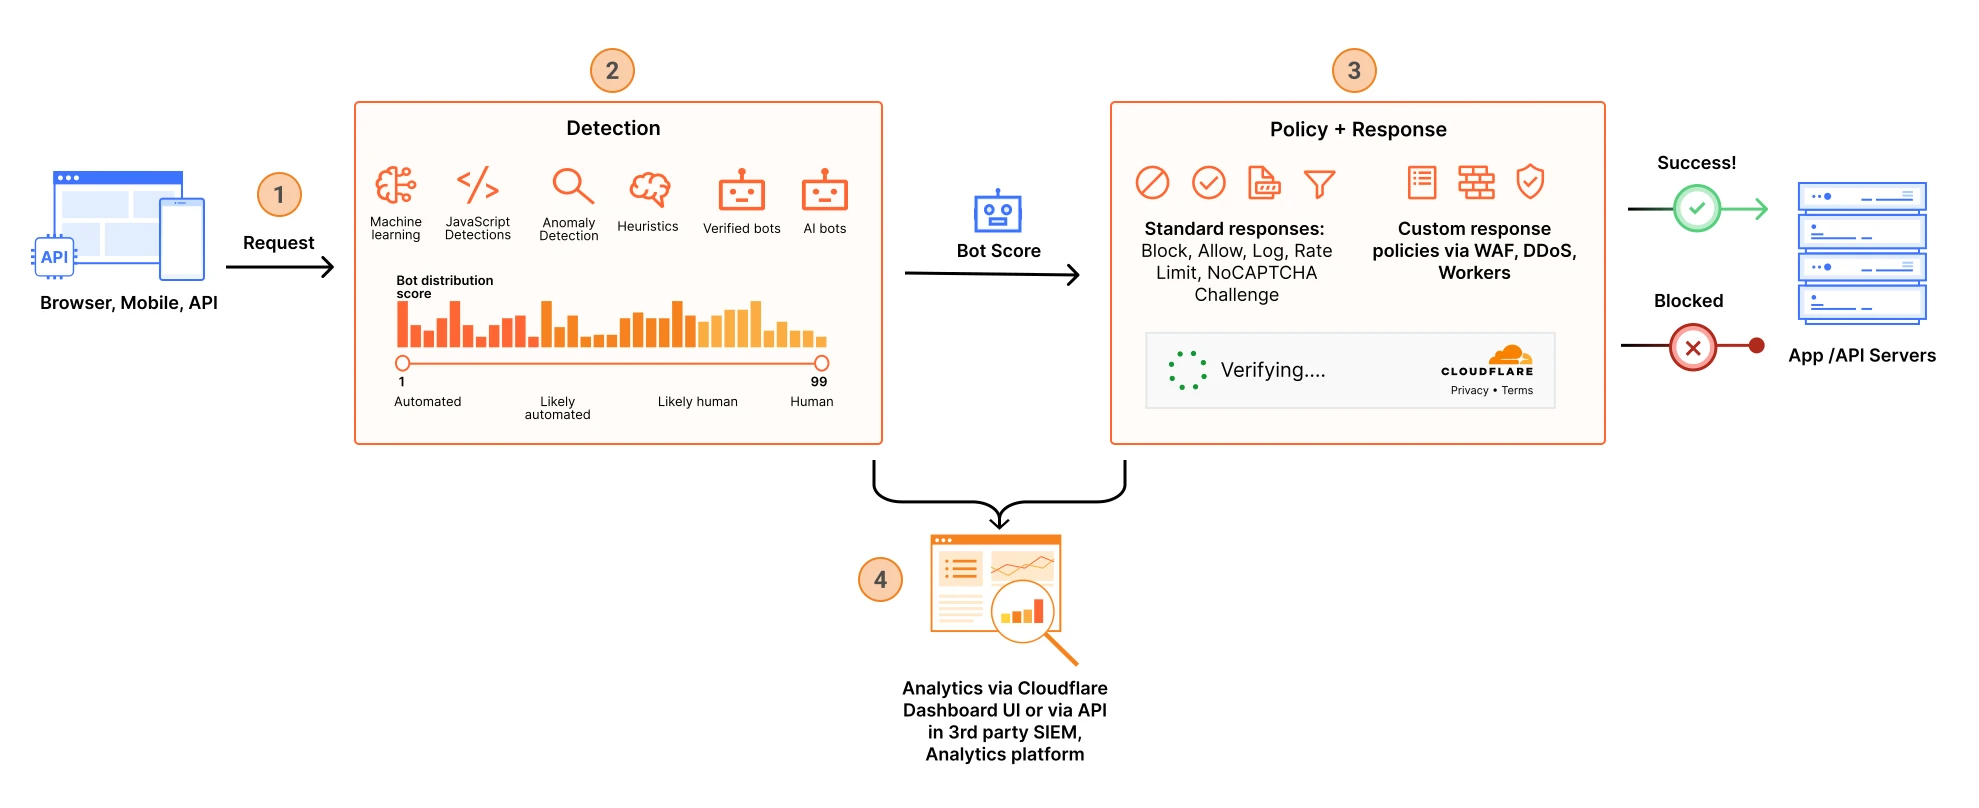
Hình 1: Cách Cloudflare nhận diện, chấm điểm và xử lý traffic từ bot.

Quản lý bot Bot management Bot management

Luồng phát hiện, chấm điểm và xử lý bot traffic trên edge — nền tảng cho WAF, rate limit và Bot Management. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots.

Thuật ngữ: Concepts: Concepts: Bot score · Super Bot Fight Mode · WAF · Rate limiting

Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Bot Bots Bots

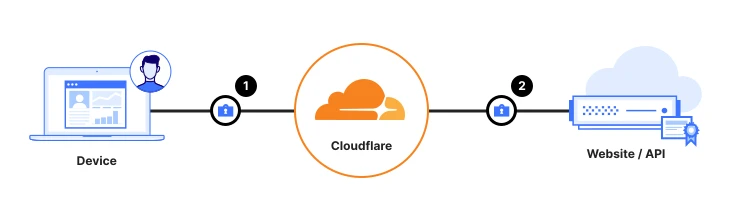
Hình 1: Bảo vệ dữ liệu từ thiết bị user đến website/API

Bảo vệ dữ liệu đang truyền (data in transit) Securing data in transit Securing data in transit

Bảo vệ data in transit với Gateway/DLP — inspect TLS traffic trước khi tới SaaS hoặc Internet. Data in transit is often considered vulnerable to interception or tampering during transmission. Data Loss Prevention (DLP) technologies can be used to inspect the contents of network traffic and block sensitive data from going to a risky destination. Data in transit is often considered vulnerable to interception or tampering during transmission. Data Loss Prevention (DLP) technologies can be used to inspect the contents of network traffic and block sensitive data from going to a risky destination.

Thuật ngữ: Concepts: Concepts: Gateway · DLP · TLS · CASB · Inline inspection

Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Bảo mật Security Security

Sau lộ trình bạn sẽ What you will achieve អ្វីដែលអ្នកនឹងសម្រេច

  • Zone Active, MX/TXT còn nguyên, screenshot rollback Zone Active, MX/TXT intact, rollback screenshot saved Zone Active, MX/TXT intact, rollback screenshot saved
  • Hostname public Proxied — curl thấy CF-Ray Public hostnames Proxied — curl shows CF-Ray Public hostnames Proxied — curl shows CF-Ray
  • Full (strict) + Always Use HTTPS; origin không bị bypass IP Full (strict) + Always Use HTTPS; origin not bypassable by IP Full (strict) + Always Use HTTPS; origin not bypassable by IP
  • WAF managed Simulate 24–48h rồi Block; rate limit /login 10 req/phút/IP WAF managed Simulate 24–48h then Block; /login rate limit 10 req/min/IP WAF managed Simulate 24–48h then Block; /login rate limit 10 req/min/IP
  • Cache Rules: bypass /admin /checkout, TTL /assets; báo cáo hit ratio + LCP Cache Rules: bypass /admin /checkout, TTL /assets; hit ratio + LCP report Cache Rules: bypass /admin /checkout, TTL /assets; hit ratio + LCP report
  • Biết khi nào mới cần API Shield, Load Balancing hoặc Waiting Room Know when you actually need API Shield, Load Balancing, or Waiting Room Know when you actually need API Shield, Load Balancing, or Waiting Room

Khái niệm cần nắm Key concepts គោលគំនិតសំខាន់

  • DNS
  • Proxy
  • SSL/TLS
  • CDN/cache
  • WAF
  • DDoS protection
  • Bot protection
  • Rate limiting
  • API security

Lỗi thường gặp Common mistakes កំហុសញឹកញាប់

Đổi nameserver trước khi review MX/TXT/DNSSEC Changing nameservers before reviewing MX/TXT/DNSSEC Changing nameservers before reviewing MX/TXT/DNSSEC

Email và xác thực domain gãy. Screenshot DNS cũ, gỡ DS nếu cần, rồi mới đổi NS. Email and domain verification break. Screenshot old DNS, remove DS if needed, then change NS. Email and domain verification break. Screenshot old DNS, remove DS if needed, then change NS.

Bật WAF/cache khi hostname còn grey-cloud Enabling WAF/cache while the hostname is grey-cloud Enabling WAF/cache while the hostname is grey-cloud

Không proxy = Cloudflare chỉ trả lời DNS. Cam trước, rồi mới rule. No proxy = Cloudflare only answers DNS. Orange-cloud first, then rules. No proxy = Cloudflare only answers DNS. Orange-cloud first, then rules.

Flexible khi origin chỉ nhận HTTPS Flexible when origin is HTTPS-only Flexible when origin is HTTPS-only

Redirect loop. Dùng Full (strict) khi origin có cert hợp lệ hoặc Origin CA. Redirect loops. Use Full (strict) when origin has a valid cert or Origin CA. Redirect loops. Use Full (strict) when origin has a valid cert or Origin CA.

WAF Block ngày đầu không Simulate WAF Block on day one with no Simulate WAF Block on day one with no Simulate

False positive trên checkout/API. Log 24–48h, tune, rồi Block. False positives on checkout/API. Log 24–48h, tune, then Block. False positives on checkout/API. Log 24–48h, tune, then Block.

Cache Everything trên HTML có session Cache Everything on session HTML Cache Everything on session HTML

User thấy giỏ hàng của nhau. Bypass /admin /checkout; cache /assets hashed. Users see each other’s carts. Bypass /admin /checkout; cache hashed /assets. Users see each other’s carts. Bypass /admin /checkout; cache hashed /assets.

Không lockdown origin No origin lockdown No origin lockdown

Attacker gọi thẳng IP, bỏ qua WAF. Allowlist IP Cloudflare hoặc Authenticated Origin Pulls. Attackers hit the origin IP and skip the WAF. Allowlist Cloudflare IPs or use Authenticated Origin Pulls. Attackers hit the origin IP and skip the WAF. Allowlist Cloudflare IPs or use Authenticated Origin Pulls.

Nội dung từng phần Module-by-module content ខ្លឹមសារតាមផ្នែក

Bắt buộc Required ចាំបាច់ ~15 phút ~15 min ~15 នាទី 1 bài 1 lessons 1 មេរៀន

Phần 0: Kiến trúc và quy trình Part 0: Architecture and workflow Part 0: Architecture and workflow

Bức tranh Visitor → proxy → SSL → WAF → cache → Origin và thứ tự xây. Đọc trước khi đổi nameserver. The picture Visitor → proxy → SSL → WAF → cache → Origin and the build order. Read before changing nameservers. រូបភាព Visitor → proxy → SSL → WAF → cache → Origin និងលំដាប់សង់។ អានមុនពេលផ្លាស់ប្តូរ nameserver។

  1. 1

    Kiến trúc Application Services và thứ tự onboarding Application Services architecture and onboarding order ស្ថាបត្យកម្ម Application Services និងលំដាប់ onboarding

    Proxy phải bật trước WAF và cache. Use case là cửa chọn — đừng rẽ API Shield hay Load Balancing trước nền. Proxy must be on before WAF and cache. Use cases are the doorway — do not branch to API Shield or Load Balancing before the spine. Proxy ត្រូវតែបើកមុន WAF និង cache។ ករណីប្រើប្រាស់គឺជាច្រកចូល — កុំបែកផ្លូវទៅ API Shield ឬ Load Balancing មុនគ្រឹះ។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
Bắt buộc Required ចាំបាច់ ~45 phút ~45 min ~45 នាទី 2 bài 2 lessons 2 មេរៀន

Phần 1: Đưa domain lên Cloudflare Part 1: Onboard your domain ផ្នែក 1: Onboard domain របស់អ្នក

Tạo zone, review DNS, đổi nameserver (hoặc CNAME setup), rồi bật proxy đúng record. Create the zone, review DNS, change nameservers (or CNAME setup), then proxy the right records. បង្កើត zone, ពិនិត្យ DNS, ផ្លាស់ប្តូរ nameserver (ឬ CNAME setup) បន្ទាប់មក proxy record ត្រឹមត្រូវ។

  1. 1

    Thêm domain và review DNS records Add domain and review DNS records បន្ថែម domain និងពិនិត្យ DNS record

    Import hoặc tạo zone cho domain. Liệt kê A/AAAA, CNAME, MX và ghi chú record nào trỏ tới origin thật. Đừng proxy MX hoặc record nội bộ không cần qua Cloudflare. Import or create a zone. List A/AAAA, CNAME, MX records and note which point to your real origin. Do not proxy MX or internal records that should not pass through Cloudflare. Import ឬបង្កើត zone។ រាយ A/AAAA, CNAME, MX record ហើយកត់ត្រាថាតើមួយណាចង្អុលទៅ origin ពិត។ កុំ proxy MX ឬ record ខាងក្នុងដែលមិនគួរឆ្លងកាត់ Cloudflare។

    Mẹo: Tip: គន្លឹះ៖ Chụp screenshot bảng DNS trước khi đổi nameserver — tiện khi rollback. Screenshot your DNS table before changing nameservers — useful for rollback. Screenshot តារាង DNS មុនពេលផ្លាស់ប្តូរ nameserver — មានប្រយោជន៍សម្រាប់ rollback។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  2. 2

    Bật proxy (orange cloud) đúng record Enable proxy on the right records បើក proxy លើ record ត្រឹមត្រូវ

    Proxy các record phục vụ HTTP/HTTPS public (website, API gateway). Giữ DNS only cho record chỉ dùng nội bộ hoặc dịch vụ đặc biệt. Proxy records serving public HTTP/HTTPS (website, API gateway). Keep DNS only for internal-only or special services. Proxy record ដែលបម្រើ HTTP/HTTPS សាធារណៈ (website, API gateway)។ រក្សា DNS only សម្រាប់សេវាខាងក្នុងតែប៉ុណ្ណោះ ឬសេវាពិសេស។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
Bắt buộc Required ចាំបាច់ ~45 phút ~45 min ~45 នាទី 2 bài 2 lessons 2 មេរៀន

Phần 2: SSL/TLS và kết nối origin Part 2: SSL/TLS and origin connection ផ្នែក 2: SSL/TLS និងការតភ្ជាប់ origin

Tránh lỗi chứng chỉ và đảm bảo traffic mã hóa end-to-end phù hợp mô hình của bạn. Avoid certificate errors and ensure encryption fits your architecture. ជៀសវាងកំហុសវិញ្ញាបនបត្រ ហើយធានាថាការអ៊ិនគ្រីបសមនឹងស្ថាបត្យកម្មរបស់អ្នក។

  1. 1

    Chọn SSL/TLS mode phù hợp Choose the right SSL/TLS mode ជ្រើសរើស SSL/TLS mode ត្រឹមត្រូវ

    Full (strict) khi origin có cert hợp lệ. Tránh Flexible nếu origin chỉ nhận HTTPS. Kiểm tra redirect HTTP→HTTPS. Use Full (strict) when origin has a valid cert. Avoid Flexible if origin expects HTTPS. Verify HTTP→HTTPS redirects. ប្រើ Full (strict) ពេល origin មាន cert ត្រឹមត្រូវ។ ជៀស Flexible បើ origin រំពឹង HTTPS។ ផ្ទៀងផ្ទាត់ HTTP→HTTPS redirect។

    Mẹo: Tip: គន្លឹះ៖ Test bằng curl hoặc browser incognito sau mỗi thay đổi mode. Test with curl or an incognito browser after each mode change. សាកល្បងដោយ curl ឬ browser incognito បន្ទាប់ពីផ្លាស់ប្តូរ mode នីមួយៗ។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  2. 2

    Origin certificate và bypass Origin certificates and bypass Origin certificate និង bypass

    Chặn truy cập trực tiếp IP origin nếu có thể (firewall chỉ cho phép Cloudflare). Điều này ngăn attacker bỏ qua WAF. Block direct origin IP access when possible (firewall allow Cloudflare only). This prevents attackers from bypassing the WAF. Block ការចូល origin IP ផ្ទាល់នៅពេលអាច (firewall អនុញ្ញាតតែ Cloudflare)។ នេះរារាំង attacker មិនឱ្យ bypass WAF។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
Bắt buộc Required ចាំបាច់ ~60 phút + 24–48h log ~60 min + 24–48h log ~60 នាទី + 24–48h log 3 bài 3 lessons 3 មេរៀន

Phần 3: Bảo mật baseline Part 3: Baseline security ផ្នែក 3: សុវត្ថិភាព baseline

WAF, DDoS, bot và rate limiting cho path quan trọng. WAF, DDoS, bots, and rate limiting for critical paths. WAF, DDoS, bot និង rate limiting សម្រាប់ path សំខាន់។

  1. 1

    Bật WAF managed rules Enable WAF managed rules បើក WAF managed rules

    Bắt đầu ở chế độ log/simulate nếu lo ngại false positive, sau đó chuyển block. Ưu tiên bảo vệ login, admin, API public. Start in log/simulate if worried about false positives, then move to block. Prioritize login, admin, and public API paths. ចាប់ផ្តើមនៅ log/Simulate បើព្រួយអំពី false positive បន្ទាប់មកផ្លាស់ប្តូរទៅ Block។ ផ្តល់អាទិភាពទៅ login, admin និង path API សាធារណៈ។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  2. 2

    Rate limiting cho login và form Rate limiting for login and forms Rate limiting សម្រាប់ login និង form

    Giới hạn request theo IP hoặc cookie cho /login, /signup, OTP, search. Giảm credential stuffing và abuse. Limit requests per IP or cookie on /login, /signup, OTP, search. Reduces credential stuffing and abuse. កំណត់ request តាម IP ឬ cookie លើ /login, /signup, OTP, search។ កាត់បន្ថយ credential stuffing និងការប្រើប្រាស់ខុស។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  3. 3

    Bot protection cơ bản Basic bot protection ការពារ bot មូលដ្ឋាន

    Phân biệt bot xấu (scrape, spam) và traffic hợp lệ. Kết hợp challenge hoặc block theo score. Separate bad bots (scraping, spam) from legitimate traffic. Combine challenges or blocks by score. បំបែក bot អាក្រក់ (scraping, spam) ពី traffic ស្របច្បាប់។ រួមបញ្ចូល challenge ឬ block តាម score។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
Khuyến nghị Recommended ណែនាំ ~90 phút ~90 min ~90 នាទី 4 bài 4 lessons 4 មេរៀន

Phần 4: Content delivery & tăng tốc website Part 4: Content delivery & website speed ផ្នែក 4: Content delivery និងល្បឿន website

CDN, cache rules, Speed, Argo/Tiered Cache và đo lường — giảm tải origin, cải thiện LCP. CDN, cache rules, Speed, Argo/Tiered Cache, and measurement — less origin load, better LCP. CDN, cache rules, Speed, Argo/Tiered Cache និងការវាស់ — កាត់បន្ថយទម្ងន់ origin, LCP ល្អជាង។

  1. 1

    CDN & cache hit/miss CDN & cache hit/miss CDN និង cache hit/miss

    Hiểu HIT tại PoP vs MISS về origin. Cache static assets; không cache HTML có session. Understand PoP HIT vs MISS to origin. Cache static assets; do not cache HTML with sessions. យល់ PoP HIT vs MISS ទៅ origin។ Cache static asset; កុំ cache HTML ដែលមាន session។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  2. 2

    Cache Rules & purge Cache Rules & purge Cache Rules និង purge

    Bypass /admin, /checkout; TTL cho /assets/*; purge sau mỗi release frontend. Bypass /admin, /checkout; TTL for /assets/*; purge after each frontend release. Bypass /admin, /checkout; TTL សម្រាប់ /assets/*; purge បន្ទាប់ពី frontend release នីមួយៗ។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  3. 3

    Speed & Images Speed & Images Speed & Images

    Brotli, Early Hints, HTTP/3; resize ảnh WebP/AVIF tại edge. Brotli, Early Hints, HTTP/3; resize images to WebP/AVIF at the edge. Brotli, Early Hints, HTTP/3; ប្តូរទំហំរូបភាពទៅ WebP/AVIF នៅ edge។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  4. 4

    Đo hit ratio & Core Web Vitals Measure hit ratio & Core Web Vitals វាស់ hit ratio និង Core Web Vitals

    Caching Analytics + Web Analytics — báo cáo trước/sau cho stakeholder. Caching Analytics + Web Analytics — before/after reports for stakeholders. Caching Analytics + Web Analytics — របាយការណ៍មុន/ក្រោយសម្រាប់ stakeholder។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
Tùy chọn Optional ស្រេចចិត្ត ~40 phút ~40 min ~40 នាទី 1 bài 1 lessons 1 មេរៀន

Phần 5: API Shield (tùy chọn) Part 5: API Shield (optional) ផ្នែក 5: API Shield (ស្រេចចិត្ត)

Sau nền zone: schema, mTLS, rate limit /api — chỉ khi use case là API. After the zone spine: schema, mTLS, /api rate limits — only when the use case is an API. បន្ទាប់ពីគ្រឹះ zone៖ schema, mTLS, rate limit /api — តែពេលករណីប្រើប្រាស់គឺ API។

  1. 1

    Bảo vệ API sau khi proxy + WAF ổn Protect APIs after proxy + WAF are stable ការពារ API បន្ទាប់ពី proxy + WAF មានស្ថិរភាព

    Free/Pro: WAF + rate limit /api + origin lockdown. Enterprise: API Shield schema, JWT, mTLS. Discover/log trước khi enforce. Free/Pro: WAF + /api rate limit + origin lockdown. Enterprise: API Shield schema, JWT, mTLS. Discover/log before enforce. Free/Pro: WAF + rate limit /api + origin lockdown។ Enterprise: API Shield schema, JWT, mTLS។ Discover/log មុនពេល enforce។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
Tùy chọn Optional ស្រេចចិត្ត ~45 phút ~45 min ~45 នាទី 1 bài 1 lessons 1 មេរៀន

Phần 6: Load Balancing và DDoS (tùy chọn) Part 6: Load Balancing and DDoS (optional) ផ្នែក 6: Load Balancing និង DDoS (ស្រេចចិត្ត)

Nhiều origin hoặc sự kiện traffic — plan-gated. DDoS L3/L4 đã có khi Proxied. Many origins or a traffic event — plan-gated. L3/L4 DDoS is already on when Proxied. origin ច្រើន ឬព្រឹត្តិការណ៍ traffic — អាស្រ័យលើ plan។ DDoS L3/L4 បើករួចហើយពេល Proxied។

  1. 1

    Pool/monitor, DDoS khi proxied, Waiting Room cho event Pools/monitors, DDoS when proxied, Waiting Room for events Pool/monitor, DDoS ពេល proxied, Waiting Room សម្រាប់ព្រឹត្តិការណ៍

    LB: health /health 60s, failover lab. Waiting Room chỉ đúng path sale/ticket. Một origin ổn — chưa cần mua LB. LB: /health every 60s, fail over in a lab. Waiting Room only on the sale/ticket path. One stable origin — do not buy LB yet. LB: /health រៀងរាល់ 60s, fail over ក្នុង lab។ Waiting Room តែនៅ path លក់/ticket។ origin ស្ថិរភាពមួយ — កុំទិញ LB នៅហ្លើយ។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
Tham chiếu Reference ឯកសារយោង Tham chiếu Reference ឯកសារយោង 2 bài 2 lessons 2 មេរៀន

Phần 7: Tham chiếu — golden rules và sổ tay Part 7: Reference — golden rules and runbook ផ្នែក 7: ឯកសារយោង — golden rules និង runbook

10 rule rollout và path dashboard / giá trị mẫu khi đã hiểu luồng. 10 rollout rules and dashboard paths / sample values once you know the flow. 10 rule rollout និង path dashboard / តម្ល័លគំរូ នៅពេលអ្នកស្គាល់លំហូរហើយ។

  1. 1

    10 golden rules Application Services 10 Application Services golden rules 10 golden rules Application Services

    Proxy trước WAF; review DNS trước đổi NS; Full (strict); lockdown origin; log rồi block; không cache session; đo rồi mới khoe. Proxy before WAF; review DNS before changing NS; Full (strict); lock down origin; log then block; no session cache; measure before celebrating. Proxy មុន WAF; ពិនិត្យ DNS មុនពេលផ្លាស់ប្តូរ NS; Full (strict); lock down origin; log បន្ទាប់មក Block; កុំ cache session; វាស់មុនពេលអបអរសាទរ។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →
  2. 2

    Sổ tay cấu hình (dashboard runbook) Configuration runbook (dashboard) runbook កំណត់រចនាសម្ព័ន្ធ (dashboard)

    Add site → DNS → Proxied → Full (strict) → Origin CA → WAF Log → /login 10/phút → Cache Rules → Analytics. Add site → DNS → Proxied → Full (strict) → Origin CA → WAF Log → /login 10/min → Cache Rules → Analytics. Add site → DNS → Proxied → Full (strict) → Origin CA → WAF Log → /login 10/min → Cache Rules → Analytics។

    Hướng dẫn chi tiết → Detailed guide → មគ្គុទេសក៍លម្អិត →

Công cụ hỗ trợ vận hành Operational tools Operational tools

Công cụ thực hành áp dụng ngay khi vận hành và xử lý sự cố. Hands-on tools to apply while operating and handling incidents. Hands-on tools to apply while operating and handling incidents.

tool

Add a site (official) Add a site (official) Add a site (ផ្លូវការ)

Onboard domain, nameserver và CNAME setup — nguồn sự thật dashboard. Onboard a domain, nameservers, and CNAME setup — dashboard source of truth. Onboard domain, nameserver និង CNAME setup — ប្រភពពិតនៅ dashboard។

tool

Application security learning path Application security learning path Application security learning path

Thứ tự chính thức: account → default traffic → WAF. Official order: account → default traffic → WAF. លំដាប់ផ្លូវការ៖ account → default traffic → WAF។

tool

DNS best practices DNS best practices DNS best practices

TTL, DNSSEC, cutover — đọc trước khi đổi nameserver production. TTL, DNSSEC, cutover — read before changing production nameservers. TTL, DNSSEC, cutover — អានមុនពេលផ្លាស់ប្តូរ nameserver production។

Trình tự học gợi ý Suggested learning order លំដាប់សិក្សាណែនាំ

  1. Đọc kiến trúc + checklist (domain, MX/TXT, path /login, plan) Read architecture + checklist (domain, MX/TXT, /login path, plan) Read architecture + checklist (domain, MX/TXT, /login path, plan)
  2. Add site, review DNS, đổi nameserver — zone Active Add site, review DNS, change nameservers — zone Active Add site, review DNS, change nameservers — zone Active
  3. Proxy hostname public; curl CF-Ray; MX grey-cloud Proxy public hostnames; curl CF-Ray; MX grey-cloud Proxy public hostnames; curl CF-Ray; MX grey-cloud
  4. Full (strict) + Always Use HTTPS; Origin CA + firewall Cloudflare IPs Full (strict) + Always Use HTTPS; Origin CA + Cloudflare IP firewall Full (strict) + Always Use HTTPS; Origin CA + Cloudflare IP firewall
  5. WAF managed Simulate 24–48h rồi Block; rate limit /login WAF managed Simulate 24–48h then Block; rate-limit /login WAF managed Simulate 24–48h then Block; rate-limit /login
  6. Cache Rules bypass /admin /checkout; TTL /assets; đo hit ratio + LCP Cache Rules bypass /admin /checkout; TTL /assets; measure hit ratio + LCP Cache Rules bypass /admin /checkout; TTL /assets; measure hit ratio + LCP
  7. Chỉ khi cần: API Shield (use case API) hoặc Load Balancing / Waiting Room Only if needed: API Shield (API use case) or Load Balancing / Waiting Room Only if needed: API Shield (API use case) or Load Balancing / Waiting Room
  8. Review golden rules; dùng runbook khi làm lại trên zone khác Review golden rules; use the runbook when repeating on another zone Review golden rules; use the runbook when repeating on another zone

Tình huống trong lộ trình Use cases for this path ករណីប្រើប្រាស់សម្រាប់ផ្លូវនេះ

Ví dụ triển khai (trong lộ trình này) Deployment examples (this path only) Deployment examples (this path only)

Tutorial và guide từ Cloudflare Resources — chỉ hiển thị nội dung phù hợp lộ trình Application Services. Mỗi bài học gợi ý 4 ví dụ riêng. Tutorials and guides from Cloudflare Resources — only content matched to the Application Services path. Each lesson suggests four examples. Tutorials and guides from Cloudflare Resources — only content matched to the Application Services path. Each lesson suggests four examples.

51 / 244
Sơ đồ kiến trúcApplication Services

Bot management

/reference-architecture/diagrams/bots/bot-management

Tìm hiểu thêm
Lộ trình họcApplication Services

Concepts

/learning-paths/dns-best-practices/concepts/

Tìm hiểu thêm
Lộ trình họcApplication Services

Concepts

/learning-paths/load-balancing/concepts/

Tìm hiểu thêm
Tài liệu mở rộng (tùy chọn) Optional extended reading Optional extended reading Mở Expand Expand GitHub, Reference Architecture, CloudSecOp, demo script — không bắt buộc. Lab guided nằm phía trên (Developer Labs). GitHub, Reference Architecture, CloudSecOp, demo scripts — not required. Guided labs sit above (Developer Labs). GitHub, Reference Architecture, CloudSecOp, demo scripts — not required. Guided labs sit above (Developer Labs).

Script demo dashboard (thực chiến) Field demo scripts (dashboard) Field demo scripts (dashboard)

Cấu hình theo nhu cầu khách hàng — đường dẫn menu, bước showcase và mẹo demo từ playbook SE. Mở rộng đầy đủ trên trang Script demo. Configure to customer needs — menu paths, showcase steps, and SE playbook tips. Full library on the Demo guides page. Configure to customer needs — menu paths, showcase steps, and SE playbook tips. Full library on the Demo guides page.

Khi nào vào mục này: Khách cần rule theo field form (SĐT, mã đơn), loại file upload, hoặc JSON key trong API.

Vị trí trên dashboard

  • Security > WAF > Custom rules
  • Security > Events

Nên xem gì

  1. Ví dụ: chặn SĐT lạm dụng

    Expression mẫu: any(http.request.body.form["billing_phone"][*] == "...") — block account spam cùng một số.

    Security > WAF > Custom rules > Create rule

  2. Giới hạn loại file upload

    POST + body match filename — chỉ cho txt/pdf/docx; exe bị 403. Test bằng curl --data-raw.

  3. Payload logging (managed rules)

    WAF > Managed rules > Configure payload logging → key pair hoặc public key → Events > Decrypt payload (trong browser, key không gửi server).

    Security > WAF > Managed rules

Lưu ý

  • Sau khi tạo rule, kiểm tra Security Events để xác nhận match/block đúng ý (có thể dùng curl hoặc request thật).

Điểm cần nhớ

  • Body inspection cho abuse cụ thể; payload logging giải thích vì sao managed ruleset bắt request.

Tài liệu chính thức: WAF custom rules · Payload logging

Tài nguyên chính thức (Resource Hub) Official resources (Resource Hub) Official resources (Resource Hub)

Liên kết từ Cloudflare Resource Hub — docs, community, case studies phù hợp track này. Links from the Cloudflare Resource Hub — docs, community, and case studies for this track. Links from the Cloudflare Resource Hub — docs, community, and case studies for this track.

Học & tài liệu Learn & docs Learn & docs Gợi ý Recommended Recommended

Developer Documentation Developer Documentation Developer Documentation

Tài liệu sản phẩm, tutorial và ví dụ cho mọi dịch vụ Cloudflare. Product docs, tutorials, and examples for every Cloudflare service. Product docs, tutorials, and examples for every Cloudflare service.

Mở trên Cloudflare Open on Cloudflare Open on Cloudflare
Học & tài liệu Learn & docs Learn & docs Trong hub In this hub In this hub Gợi ý Recommended Recommended

Learning Center Learning Center Learning Center

Giải thích khái niệm và hướng dẫn thực hành cho kiến trúc web hiện đại. Concept explainers and practical guides for modern web architecture. Concept explainers and practical guides for modern web architecture.

Xem trong hub View in hub View in hub
Học & tài liệu Learn & docs Learn & docs Trong hub In this hub In this hub Gợi ý Recommended Recommended

Reference Architectures Reference Architectures Reference Architectures

Pattern kiến trúc và best practices — SASE, CDN, Workers, Zero Trust. Architecture patterns and best practices — SASE, CDN, Workers, Zero Trust. Architecture patterns and best practices — SASE, CDN, Workers, Zero Trust.

Xem trong hub View in hub View in hub
Cộng đồng & cập nhật Community & updates Community & updates Trong hub In this hub In this hub Gợi ý Recommended Recommended

Developer Changelog Developer Changelog Developer Changelog

Cập nhật sản phẩm theo ngày — Agents, Workers, Cloudflare One, R2, security. Hub có bản tóm tắt chọn lọc. Daily product updates — Agents, Workers, Cloudflare One, R2, security. This hub includes a curated summary. Daily product updates — Agents, Workers, Cloudflare One, R2, security. This hub includes a curated summary.

Xem trong hub View in hub View in hub

Chủ đề Learning Center Learning Center topics Learning Center topics

Kiến trúc tham chiếu Reference Architecture Reference Architecture

Sơ đồ và tài liệu thiết kế chính thức từ Cloudflare Architecture Center — bổ sung lộ trình học trong hub. Official design diagrams and docs from the Cloudflare Architecture Center — complementing this track in the hub. Official design diagrams and docs from the Cloudflare Architecture Center — complementing this track in the hub.

Kiến trúc tham chiếu Reference architecture Reference architecture Nổi bật Featured Featured Lộ trình: Track: Track: Application Services

Kiến trúc bảo mật Cloudflare Cloudflare Security Architecture Cloudflare Security Architecture

Cách mạng và nền tảng Cloudflare được thiết kế về security, vận hành và dịch vụ cho doanh nghiệp. How Cloudflare’s network and platform are designed for security, operations, and enterprise services. How Cloudflare’s network and platform are designed for security, operations, and enterprise services.

Figure 1: Data flow overview
Kiến trúc tham chiếu Reference architecture Reference architecture Nổi bật Featured Featured Lộ trình: Track: Track: Application Services

Kiến trúc tham chiếu CDN CDN Reference Architecture CDN Reference Architecture

Thách thức web app truyền thống, cách CDN Cloudflare giải quyết, và thiết kế kiến trúc CDN. Traditional web app challenges, how Cloudflare CDN solves them, and CDN architecture design. Traditional web app challenges, how Cloudflare CDN solves them, and CDN architecture design.

Hướng dẫn thiết kế Design guide Design guide Nổi bật Featured Featured Lộ trình: Track: Track: Application Services

Phân phối ứng dụng an toàn với Cloudflare Securely deliver applications with Cloudflare Securely deliver applications with Cloudflare

Bộ dịch vụ performance, security, reliability, development và Zero Trust cho ứng dụng. Performance, security, reliability, development, and Zero Trust services for applications. Performance, security, reliability, development, and Zero Trust services for applications.

Kiến trúc tham chiếu Reference architecture Reference architecture Lộ trình: Track: Track: Application Services

Kiến trúc tham chiếu Load Balancing Load Balancing Reference Architecture Load Balancing Reference Architecture

Global và local traffic management — cho team vận hành web, hosting và network. Global and local traffic management — for web, hosting, and network teams. Global and local traffic management — for web, hosting, and network teams.

Ví dụ từ GitHub Cloudflare Examples from Cloudflare GitHub Examples from Cloudflare GitHub

Repo open source chính thức trên github.com/cloudflare — học bằng README và code mẫu. Official open source at github.com/cloudflare — learn from READMEs and sample code. Official open source at github.com/cloudflare — learn from READMEs and sample code.

Ví dụ 4: Transform HTML tại edge Example 4: Transform HTML at the edge Example 4: Transform HTML at the edge

lol-html + Workers — CSP nonce, rewrite URL — bảo mật Application Services. lol-html + Workers — CSP nonce, URL rewrite — Application Services security. lol-html + Workers — CSP nonce, URL rewrite — Application Services security.

Pinned Pinned Pinned Hạ tầng & Core Infrastructure & Core Infrastructure & Core Rust ★ 11,500

cloudflare/quiche

Implementation QUIC + HTTP/3 — giao thức hiện đại cho web nhanh và mã hóa. QUIC and HTTP/3 implementation — modern protocol for fast, encrypted web. QUIC and HTTP/3 implementation — modern protocol for fast, encrypted web.

Gợi ý học / thử: Try this: Try this:

Đọc để hiểu vì sao HTTP/3 và QUIC liên quan performance Application Services. Read to understand how HTTP/3 and QUIC relate to Application Services performance. Read to understand how HTTP/3 and QUIC relate to Application Services performance.

Mở trên GitHub Open on GitHub Open on GitHub
Hạ tầng & Core Infrastructure & Core Infrastructure & Core Rust ★ 2,006

cloudflare/lol-html

Streaming HTML parser/rewriter với CSS selector — dùng trong Workers. Streaming HTML parser/rewriter with CSS selectors — used in Workers. Streaming HTML parser/rewriter with CSS selectors — used in Workers.

Gợi ý học / thử: Try this: Try this:

Thử rewrite HTML tại edge (nonce CSP, inject analytics) — liên kết bài CloudSecOp lol-html. Try edge HTML rewrite (CSP nonce, analytics inject) — pairs with the CloudSecOp lol-html post. Try edge HTML rewrite (CSP nonce, analytics inject) — pairs with the CloudSecOp lol-html post.

Mở trên GitHub Open on GitHub Open on GitHub
Hạ tầng & Core Infrastructure & Core Infrastructure & Core Go ★ 1,671

cloudflare/circl

Thư viện crypto tái sử dụng — post-quantum và curve hiện đại. Interoperable cryptographic library — post-quantum and modern curves. Interoperable cryptographic library — post-quantum and modern curves.

Gợi ý học / thử: Try this: Try this:

Đọc overview để hiểu TLS/crypto layer — bổ sung khái niệm SSL/TLS trong lộ trình Application Services. Read the overview for TLS/crypto context — complements SSL/TLS in the Application Services track. Read the overview for TLS/crypto context — complements SSL/TLS in the Application Services track.

Mở trên GitHub Open on GitHub Open on GitHub
Ví dụ & Demo Examples & Demos Examples & Demos JavaScript ★ 697

cloudflare/speedtest

Component đo tốc độ mạng tới edge Cloudflare. Component to measure network speed against Cloudflare’s edge. Component to measure network speed against Cloudflare’s edge.

Gợi ý học / thử: Try this: Try this:

Nhúng widget speedtest vào trang demo → giải thích CDN/edge proximity cho stakeholder. Embed the speedtest widget on a demo page → explain CDN/edge proximity to stakeholders. Embed the speedtest widget on a demo page → explain CDN/edge proximity to stakeholders.

Mở trên GitHub Open on GitHub Open on GitHub

Đọc thêm — kinh nghiệm thực tế (CloudSecOp) Further reading — field notes (CloudSecOp) Further reading — field notes (CloudSecOp)

Bài viết từ cloudsecop.net — bổ sung lộ trình hub với context triển khai production, không thay tài liệu chính thức Cloudflare. Posts from cloudsecop.net — complement this track with production deployment context; not a replacement for official Cloudflare docs. Posts from cloudsecop.net — complement this track with production deployment context; not a replacement for official Cloudflare docs.

7 phút đọc 7 min read 7 min read

lol-html: streaming HTML rewriter trên Workers — 3 production patterns lol-html streaming HTML rewriter on Workers lol-html streaming HTML rewriter on Workers

CSP nonce per request, rewrite analytics URL, A/B inject tại edge. Per-request CSP nonce, analytics URL rewrite, A/B inject at the edge. Per-request CSP nonce, analytics URL rewrite, A/B inject at the edge.

  • Workers
  • HTML
Đọc trên CloudSecOp Read on CloudSecOp Read on CloudSecOp
9 phút đọc 9 min read 9 min read

Pingora vs AWS ALB/NLB Pingora vs AWS ALB/NLB Pingora vs AWS ALB/NLB

Khi nào self-host reverse proxy bằng pingora-core thắng ALB managed. When self-hosted pingora-core beats managed ALB. When self-hosted pingora-core beats managed ALB.

  • Pingora
Đọc trên CloudSecOp Read on CloudSecOp Read on CloudSecOp
Phần 18 Part 18 Part 18 8 phút đọc 8 min read 8 min read

Security cho Worker: secrets, CSP, Bot Management, Turnstile Worker security: secrets, CSP, Bot Management, Turnstile Worker security: secrets, CSP, Bot Management, Turnstile

Defense-in-depth: WAF, Turnstile, Access JWT, Zod validation, anti-pattern. Defense-in-depth: WAF, Turnstile, Access JWT, Zod validation, anti-patterns. Defense-in-depth: WAF, Turnstile, Access JWT, Zod validation, anti-patterns.

  • security
  • Turnstile
Đọc trên CloudSecOp Read on CloudSecOp Read on CloudSecOp
Phần 17 Part 17 Part 17 9 phút đọc 9 min read 9 min read

Observability cho Worker: Logs, Tail Workers, Analytics Worker observability: Logs, Tail Workers, Analytics Worker observability: Logs, Tail Workers, Analytics

4 tầng: Workers Logs, Tail, Logpush, Analytics Engine — debug production. Four layers: Workers Logs, Tail, Logpush, Analytics Engine — production debugging. Four layers: Workers Logs, Tail, Logpush, Analytics Engine — production debugging.

  • observability
Đọc trên CloudSecOp Read on CloudSecOp Read on CloudSecOp

Bước tiếp theo Next step Next step

Áp dụng ngay qua tình huống thực tế và checklist. Apply what you learned via a use case and checklist. Apply what you learned via a use case and checklist.

Học xong hoặc muốn đổi hướng? Finished or want a different path? Finished or want a different path?

Ba lộ trình độc lập — mỗi lộ trình chỉ gồm bài học và tài liệu trong phạm vi đó. Chọn lộ trình khác khi sẵn sàng, không cần học song song. Three independent paths — each includes only lessons and materials for that scope. Switch when you are ready; no need to study paths in parallel. Three independent paths — each includes only lessons and materials for that scope. Switch when you are ready; no need to study paths in parallel.

Chưa chắc — làm bài chọn lộ trình Not sure — use the path selector Not sure — use the path selector · So sánh cả ba lộ trình Compare all three paths Compare all three paths