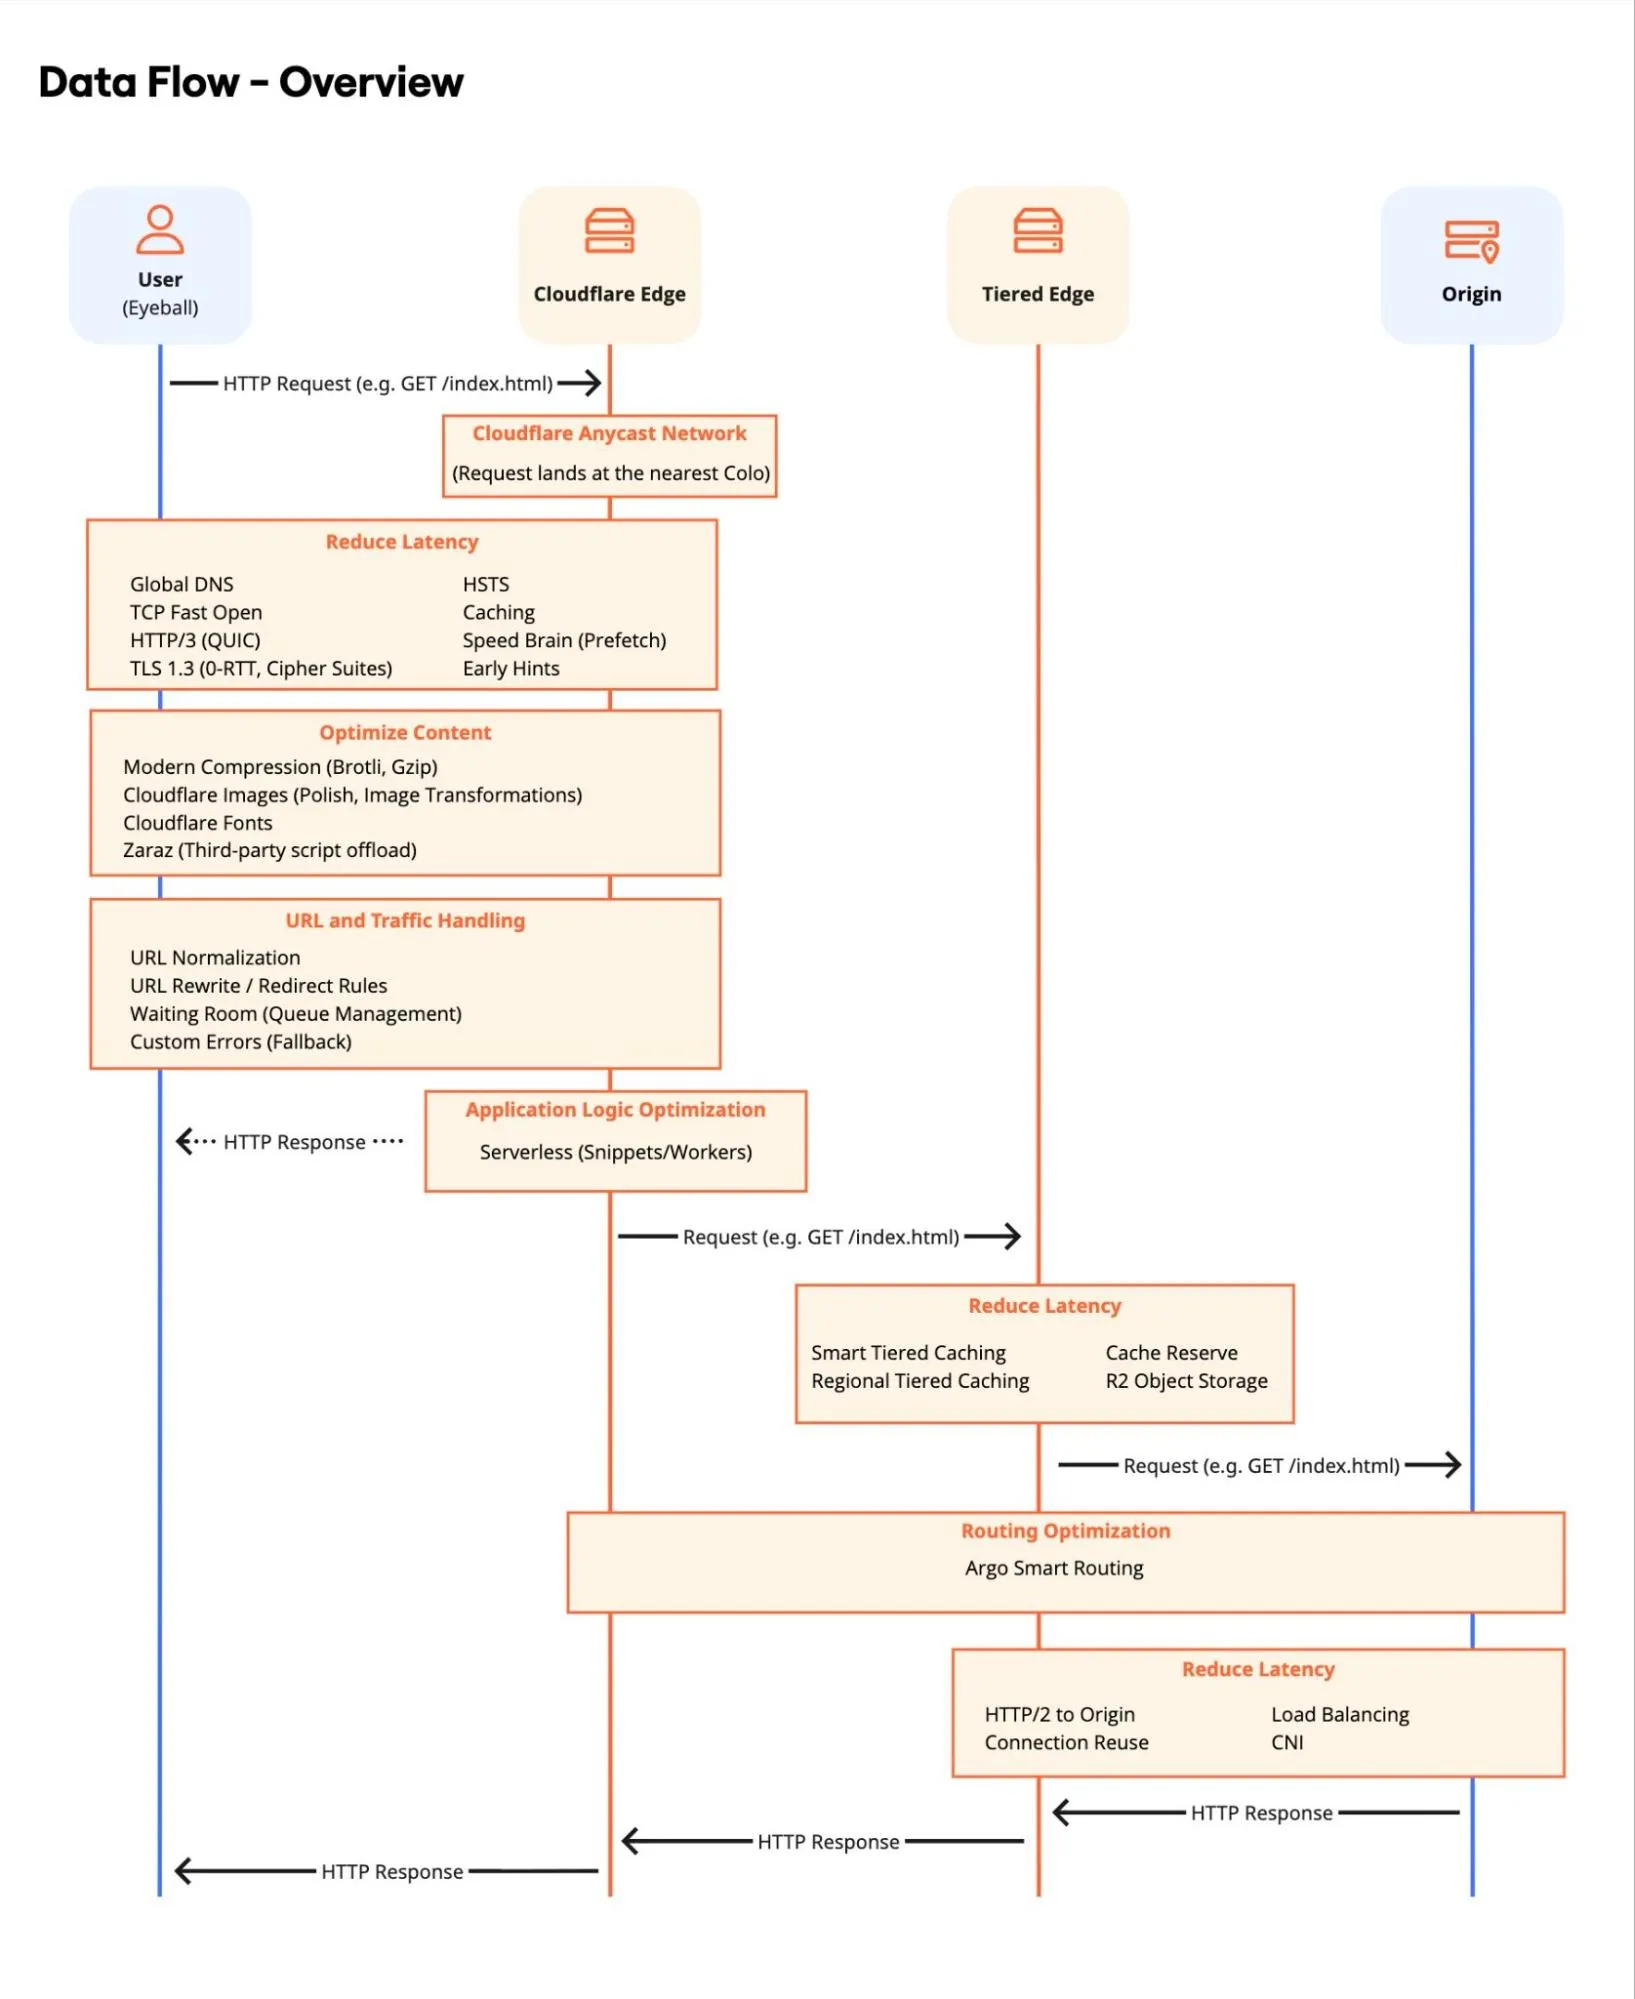
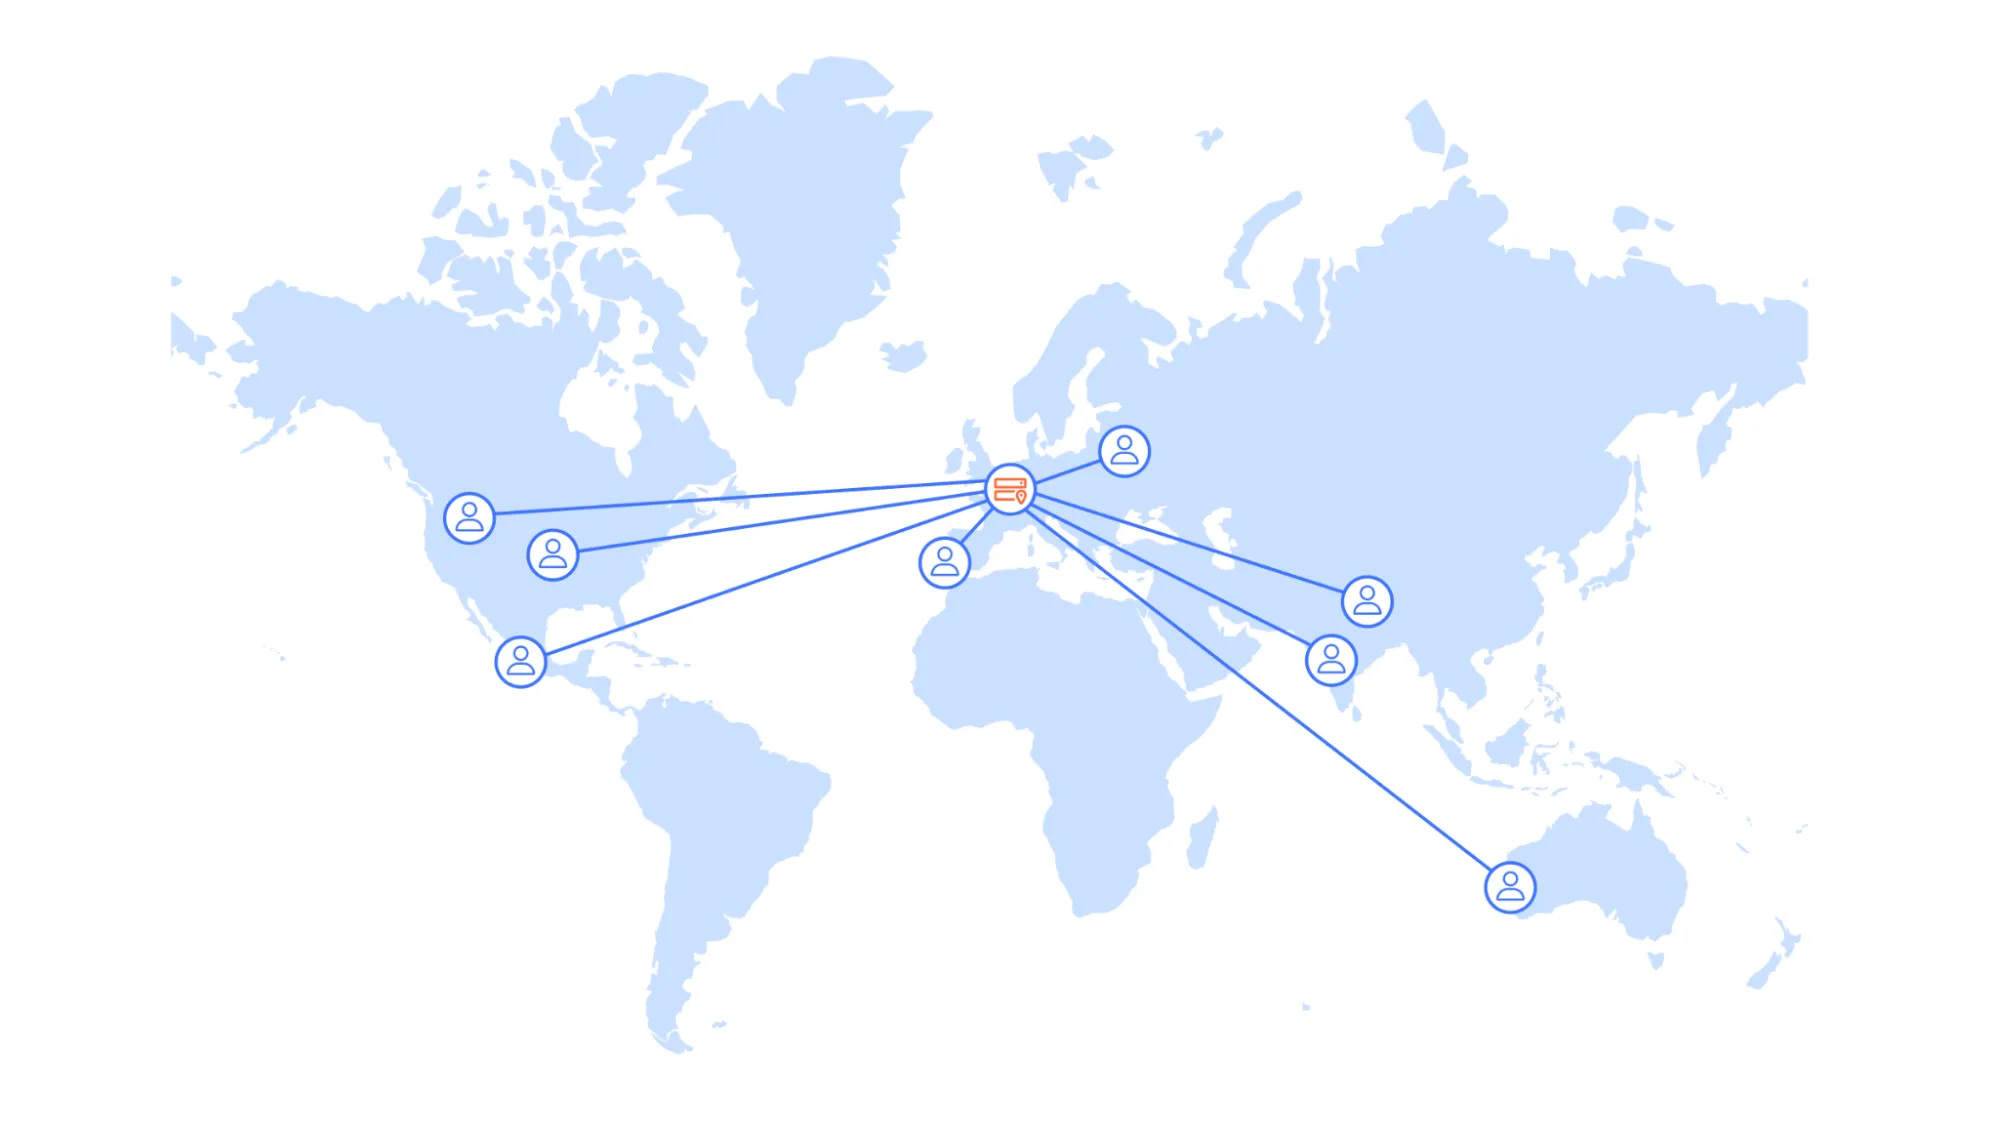
Rate limiting: chặn spam form và dò mật khẩu đơn giản Rate limiting: a simple brake on form spam and password guessing Rate limiting៖ របាំងសាមញ្ញបញ្ហ spam form និងការទាយពាក្យសម្ងាត់
Spam form và brute-force login không cần hack phức tạp — chỉ cần gửi nhiều request. Rate limiting là “cửa sổ đếm”: quá N lần trong T giây thì chặn hoặc challenge. Form spam and login brute force do not need fancy hacks — just many requests. Rate limiting is a “counting window”: more than N times in T seconds means block or challenge. Spam form និង brute-force login មិនត្រូវការ hack ស្មុគស្មាញ — គ្រាន់តែ request ច្រើន។ Rate limiting គឺ "បង្អួចរាប់"៖ លើស N ដងក្នុង T វិនាទី នោះ block ឬ challenge។
Quản lý bot Bot management Bot management
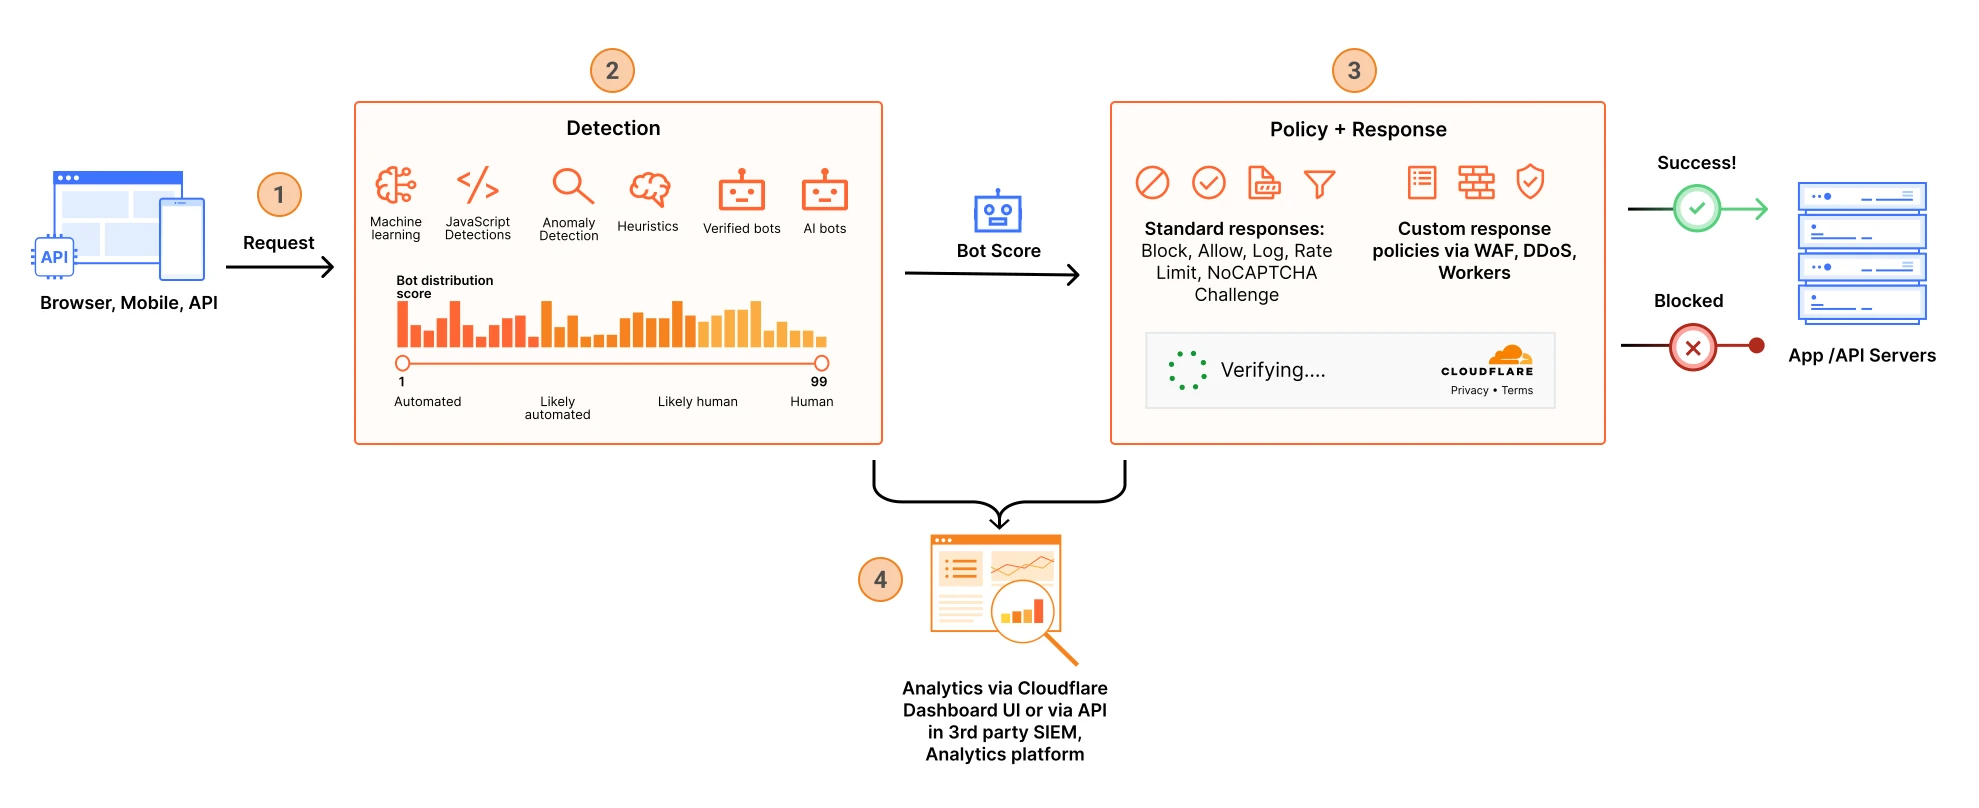
Luồng phát hiện, chấm điểm và xử lý bot traffic trên edge — nền tảng cho WAF, rate limit và Bot Management. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots.
Thuật ngữ: Concepts: Concepts: Bot score · Super Bot Fight Mode · WAF · Rate limiting
Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Bot Bots Bots
Rate limiting giải quyết vấn đề gì? What problem does rate limiting solve? What problem does rate limiting solve?
Hình dung form đăng ký workshop hoặc trang login: attacker (hoặc bot) gửi hàng nghìn request trong vài phút — spam database, làm chậm origin, hoặc thử từng mật khẩu trong danh sách. Server gốc phải xử lý mỗi request; không có giới hạn, một IP có thể “ăn” tài nguyên như hàng trăm user thật. Picture a workshop signup form or login page: an attacker (or bot) sends thousands of requests in minutes — spamming the database, slowing the origin, or trying passwords from a list. The origin must handle each request; without limits, one IP can consume resources like hundreds of real users. Picture a workshop signup form or login page: an attacker (or bot) sends thousands of requests in minutes — spamming the database, slowing the origin, or trying passwords from a list. The origin must handle each request; without limits, one IP can consume resources like hundreds of real users.
Rate limiting đặt quy tắc: ví dụ “mỗi IP chỉ được 10 request POST tới `/api/login` trong 60 giây”. Vượt ngưỡng → block, challenge (Turnstile), hoặc log. Cloudflare áp dụng ở edge — trước khi request chạm origin — giống lễ tân không cho cùng một người gõ cửa liên tục. Rate limiting sets a rule: for example “each IP may only POST to `/api/login` 10 times per 60 seconds.” Above the threshold → block, challenge (Turnstile), or log. Cloudflare applies this at the edge — before the request hits the origin — like a receptionist stopping the same person from knocking endlessly. Rate limiting sets a rule: for example “each IP may only POST to `/api/login` 10 times per 60 seconds.” Above the threshold → block, challenge (Turnstile), or log. Cloudflare applies this at the edge — before the request hits the origin — like a receptionist stopping the same person from knocking endlessly.
Trên blog.cloudflare.com, bài security và WAF thường nhắc rate limiting cùng bot management: không phải silver bullet, nhưng là lớp rẻ và hiệu quả cho abuse phổ biến. Hub có trang sản phẩm Rate limiting và lộ trình Application Services. On blog.cloudflare.com, security and WAF posts often mention rate limiting alongside bot management: not a silver bullet, but a cheap effective layer for common abuse. The hub has a Rate limiting product page and Application Services track. On blog.cloudflare.com, security and WAF posts often mention rate limiting alongside bot management: not a silver bullet, but a cheap effective layer for common abuse. The hub has a Rate limiting product page and Application Services track.
Quản lý bot Bot management Bot management
Luồng phát hiện, chấm điểm và xử lý bot traffic trên edge — nền tảng cho WAF, rate limit và Bot Management. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots. Cloudflare has bot management capabilities to help identify and mitigate automated traffic to protect domains from bad bots.
Thuật ngữ: Concepts: Concepts: Bot score · Super Bot Fight Mode · WAF · Rate limiting
Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Bot Bots Bots
Giới hạn theo IP, path và kết hợp WAF Limits by IP, path, and combining with WAF Limits by IP, path, and combining with WAF
Theo IP: phổ biến nhất — mỗi địa chỉ nguồn có ngưỡng riêng. Theo path: `/api/signup` nghiêm hơn `/` vì abuse tập trung endpoint. Theo header hoặc API key khi bạn có client đã xác thực — tránh một partner API làm quá tải. By IP: most common — each source address gets its own threshold. By path: `/api/signup` stricter than `/` because abuse targets endpoints. By header or API key when you have authenticated clients — so one partner API cannot overload you. By IP: most common — each source address gets its own threshold. By path: `/api/signup` stricter than `/` because abuse targets endpoints. By header or API key when you have authenticated clients — so one partner API cannot overload you.
WAF (Web Application Firewall) lọc payload xấu (SQL injection, XSS); rate limiting lọc volume. Form login thường cần cả hai: WAF chặn payload lạ, rate limit chặn volume cao. Tutorial Turnstile + WAF + Bot Management trên docs Cloudflare minh họa stack cho login — hub trỏ tới use case bảo vệ website. A WAF filters bad payloads (SQL injection, XSS); rate limiting filters volume. Login forms often need both: WAF blocks weird payloads, rate limits block high volume. The Turnstile + WAF + Bot Management tutorial on Cloudflare docs illustrates the login stack — the hub points to protect-website use cases. A WAF filters bad payloads (SQL injection, XSS); rate limiting filters volume. Login forms often need both: WAF blocks weird payloads, rate limits block high volume. The Turnstile + WAF + Bot Management tutorial on Cloudflare docs illustrates the login stack — the hub points to protect-website use cases.
Super Bot Fight Mode hoặc Bot Management (tùy gói) thêm điểm số bot — rate limit theo `cf.bot_management.score` khi bạn cần rule tinh hơn “chặn mọi IP”. Sơ đồ bot-management trên reference architecture gắn bots, WAF, và rate limiting trong một bức tranh. Super Bot Fight Mode or Bot Management (plan-dependent) add bot scores — rate limit by `cf.bot_management.score` when you need finer rules than “block every IP.” The bot-management reference architecture diagram ties bots, WAF, and rate limiting into one picture. Super Bot Fight Mode or Bot Management (plan-dependent) add bot scores — rate limit by `cf.bot_management.score` when you need finer rules than “block every IP.” The bot-management reference architecture diagram ties bots, WAF, and rate limiting into one picture.
False positive: đừng chặn user thật sau chiến dịch marketing False positives: do not block real users after a marketing campaign False positives: do not block real users after a marketing campaign
Rate limit quá chặt có thể chặn công ty (một IP outbound) hoặc trường học — nhiều user cùng IP. Giải pháp: ngưỡng cao hơn cho GET, chặt hơn cho POST login; whitelist IP nội bộ nếu cần; dùng challenge thay vì block cứng để user thật vượt qua Turnstile. Overly tight limits can block a company (one outbound IP) or a school — many users share one IP. Fixes: higher thresholds for GET, stricter for POST login; whitelist internal IPs if needed; use challenge instead of hard block so real users pass Turnstile. Overly tight limits can block a company (one outbound IP) or a school — many users share one IP. Fixes: higher thresholds for GET, stricter for POST login; whitelist internal IPs if needed; use challenge instead of hard block so real users pass Turnstile.
Luôn monitor sau khi bật rule mới: dashboard Security Events cho biết rule nào kích hoạt bao nhiêu. Nếu spike block trùng giờ traffic marketing, hãy điều chỉnh ngưỡng hoặc thêm exception có thời hạn. Always monitor after enabling a new rule: Security Events dashboard shows which rules fire how often. If block spikes match marketing traffic hours, adjust thresholds or add a time-bound exception. Always monitor after enabling a new rule: Security Events dashboard shows which rules fire how often. If block spikes match marketing traffic hours, adjust thresholds or add a time-bound exception.
Workshop signup trên hub dùng Turnstile dev-bypass local — production nên có Turnstile thật + rate limit trên endpoint signup. Đó là mô hình defense in depth cho form public. Workshop signup on this hub uses Turnstile dev-bypass locally — production should have real Turnstile + rate limits on the signup endpoint. That is a defense-in-depth model for public forms. Workshop signup on this hub uses Turnstile dev-bypass locally — production should have real Turnstile + rate limits on the signup endpoint. That is a defense-in-depth model for public forms.
Bắt đầu với hai rule đơn giản Start with two simple rules Start with two simple rules
Rule 1: POST tới `/login` hoặc `/api/auth/*` — ví dụ 10 request / phút / IP, action block hoặc challenge. Rule 2: POST tới form public (signup, contact) — ví dụ 20 request / phút / IP. Ghi log trước khi block cứng nếu bạn chưa chắc ngưỡng. Rule 1: POST to `/login` or `/api/auth/*` — e.g. 10 requests per minute per IP, action block or challenge. Rule 2: POST to public forms (signup, contact) — e.g. 20 requests per minute per IP. Log before hard block if you are unsure of thresholds. Rule 1: POST to `/login` or `/api/auth/*` — e.g. 10 requests per minute per IP, action block or challenge. Rule 2: POST to public forms (signup, contact) — e.g. 20 requests per minute per IP. Log before hard block if you are unsure of thresholds.
Đọc trang Rate limiting và WAF trên hub; bài WAF cho người mới giải thích lớp bảo vệ chung. Khi cần sâu hơn, mở blog.cloudflare.com/tag/security/ và docs rate limiting rules. Read Rate limiting and WAF pages on the hub; the beginner WAF post explains the general protection layer. For depth, open blog.cloudflare.com/tag/security/ and rate limiting rules docs. Read Rate limiting and WAF pages on the hub; the beginner WAF post explains the general protection layer. For depth, open blog.cloudflare.com/tag/security/ and rate limiting rules docs.
Hình minh họa Cloudflare Cloudflare visuals Cloudflare visuals
Sơ đồ Reference Architecture chính thức và (khi có) ảnh Dashboard — giúp đối chiếu khi học. Official Reference Architecture diagrams and (when available) Dashboard screenshots — useful while you learn. Official Reference Architecture diagrams and (when available) Dashboard screenshots — useful while you learn.
Bảo vệ dữ liệu đang truyền (data in transit) Securing data in transit Securing data in transit
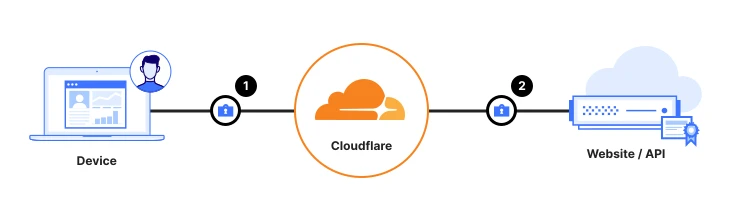
Bảo vệ data in transit với Gateway/DLP — inspect TLS traffic trước khi tới SaaS hoặc Internet. Data in transit is often considered vulnerable to interception or tampering during transmission. Data Loss Prevention (DLP) technologies can be used to inspect the contents of network traffic and block sensitive data from going to a risky destination. Data in transit is often considered vulnerable to interception or tampering during transmission. Data Loss Prevention (DLP) technologies can be used to inspect the contents of network traffic and block sensitive data from going to a risky destination.
Thuật ngữ: Concepts: Concepts: Gateway · DLP · TLS · CASB · Inline inspection
Sơ đồ chính thức ↗ Official diagram ↗ Official diagram ↗ · Bảo mật Security Security
Câu hỏi thường gặp Frequently asked questions Frequently asked questions
Rate limiting có thay Turnstile không? Can rate limiting replace Turnstile? Can rate limiting replace Turnstile?
Không hoàn toàn. Rate limit chặn volume; Turnstile phân biệt human vs bot tốt hơn cho form. Nhiều site dùng cả hai. Not fully. Rate limits stop volume; Turnstile better separates humans from bots on forms. Many sites use both. Not fully. Rate limits stop volume; Turnstile better separates humans from bots on forms. Many sites use both.
Rate limiting áp dụng cho API Workers không? Does rate limiting apply to Workers APIs? Does rate limiting apply to Workers APIs?
Có — qua WAF rate limiting rules trên zone proxy, hoặc logic rate limit trong Worker (KV/Durable Objects) cho API riêng. Chọn theo mức độ kiểm soát bạn cần. Yes — via WAF rate limiting rules on a proxied zone, or rate limit logic in a Worker (KV/Durable Objects) for custom APIs. Choose based on control you need. Yes — via WAF rate limiting rules on a proxied zone, or rate limit logic in a Worker (KV/Durable Objects) for custom APIs. Choose based on control you need.
Free plan có rate limiting không? Is rate limiting on the Free plan? Is rate limiting on the Free plan?
Tính năng và ngưỡng phụ thuộc gói Cloudflare — xem pricing và docs hiện tại. Người mới vẫn nên đọc rule templates và Security Events dù ở gói thấp. Features and thresholds depend on your Cloudflare plan — check current pricing and docs. Beginners should still read rule templates and Security Events even on lower tiers. Features and thresholds depend on your Cloudflare plan — check current pricing and docs. Beginners should still read rule templates and Security Events even on lower tiers.
Học tiếp trên hub (on-page backlinks) Keep learning on this hub (on-page links) Keep learning on this hub (on-page links)
- Rate limiting (trang sản phẩm) Rate limiting (product page) Rate limiting (product page)
- WAF (trang sản phẩm) WAF (product page) WAF (product page)
- Use case: bảo vệ website Use case: protect a website Use case: protect a website
- Lộ trình Application Services Application Services track Application Services track
- Turnstile cho form Turnstile for forms Turnstile for forms
Nguồn tham khảo (blog.cloudflare.com) Sources (blog.cloudflare.com) Sources (blog.cloudflare.com)
Nội dung được viết lại để dễ hiểu hơn; luôn đọc bài gốc trên blog.cloudflare.com và docs chính thức khi cần chi tiết kỹ thuật hoặc cập nhật mới nhất. Content is rewritten for clarity; always read the original posts on blog.cloudflare.com and official docs for technical detail or the latest updates. Content is rewritten for clarity; always read the original posts on blog.cloudflare.com and official docs for technical detail or the latest updates.